Search vulnerabilities

Results 428,381

CVE-2025-0786

ESAFENET CDG appDetail.jsp sql injection

A vulnerability was found in ESAFENET CDG V5. It has been classified as critical. Affected is an unknown function of the file /appDetail.jsp. The manipulation of the argument flowId leads to sql injection. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. The vendor was contacted early about this disclosure but did not respond in any way.

CVSS 4.0 · 5.3 Medium EPSS < 1% KEV · Not listed
Vendors
Products
Cdg
CVE-2025-0785

ESAFENET CDG SysConfig.jsp cross site scripting

A vulnerability was found in ESAFENET CDG V5 and classified as problematic. This issue affects some unknown processing of the file /SysConfig.jsp. The manipulation of the argument help leads to cross site scripting. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The vendor was contacted early about this disclosure but did not respond in any way.

CVSS 4.0 · 5.3 Medium EPSS < 1% KEV · Not listed
Vendors
Products
Cdg
CVE-2024-9536

ESAFENET CDG MultiServerBackService sql injection

A vulnerability was found in ESAFENET CDG V5. It has been rated as critical. Affected by this issue is some unknown functionality of the file /MultiServerBackService?path=1. The manipulation of the argument fileId leads to sql injection. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. The vendor was contacted early about this disclosure but did not respond in any way.

CVSS 4.0 · 5.3 Medium EPSS < 1% KEV · Not listed
Vendors
Products
Cdg
CVE-2025-3240

PHPGurukul Online Fire Reporting System search.php sql injection

A vulnerability, which was classified as critical, has been found in PHPGurukul Online Fire Reporting System 1.2. Affected by this issue is some unknown functionality of the file /admin/search.php. The manipulation of the argument searchdata leads to sql injection. The attack may be launched remotely. The exploit has been disclosed to the public and may be used.

CVSS 4.0 · 6.9 Medium EPSS < 1% KEV · Not listed
Vendors
CVE-2025-3377

PCMan FTP Server ENC Command buffer overflow

A vulnerability was found in PCMan FTP Server 2.0.7. It has been rated as critical. This issue affects some unknown processing of the component ENC Command Handler. The manipulation leads to buffer overflow. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used.

CVSS 4.0 · 6.9 Medium EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-3376

PCMan FTP Server CONF Command buffer overflow

A vulnerability was found in PCMan FTP Server 2.0.7. It has been declared as critical. This vulnerability affects unknown code of the component CONF Command Handler. The manipulation leads to buffer overflow. The attack can be initiated remotely. The exploit has been disclosed to the public and may be used.

CVSS 4.0 · 6.9 Medium EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-3375

PCMan FTP Server CDUP Command buffer overflow

A vulnerability was found in PCMan FTP Server 2.0.7. It has been classified as critical. This affects an unknown part of the component CDUP Command Handler. The manipulation leads to buffer overflow. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used.

CVSS 4.0 · 6.9 Medium EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-3373

PCMan FTP Server SITE CHMOD Command buffer overflow

A vulnerability has been found in PCMan FTP Server 2.0.7 and classified as critical. Affected by this vulnerability is an unknown functionality of the component SITE CHMOD Command Handler. The manipulation leads to buffer overflow. The attack can be launched remotely. The exploit has been disclosed to the public and may be used.

CVSS 4.0 · 6.9 Medium EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-3372

PCMan FTP Server MKDIR Command buffer overflow

A vulnerability, which was classified as critical, was found in PCMan FTP Server 2.0.7. Affected is an unknown function of the component MKDIR Command Handler. The manipulation leads to buffer overflow. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used.

CVSS 4.0 · 6.9 Medium EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-4497

code-projects Simple Banking System Sign In buffer overflow

A vulnerability was found in code-projects Simple Banking System up to 1.0. It has been rated as critical. This issue affects some unknown processing of the component Sign In. The manipulation of the argument password2 leads to buffer overflow. Attacking locally is a requirement. The exploit has been disclosed to the public and may be used.

CVSS 4.0 · 4.8 Medium EPSS < 1% KEV · Not listed
Vendors
CVE-2025-26492

In JetBrains TeamCity before 2024.12.2 improper Kubernetes connection settings could expose sensitive resources

CVSS 3.1 · 7.7 High EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-26493

In JetBrains TeamCity before 2024.12.2 several DOM-based XSS were possible on the Code Inspection Report tab

CVSS 3.1 · 4.6 Medium EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-31139

In JetBrains TeamCity before 2025.03 base64 encoded password could be exposed in build log

CVSS 3.1 · 4.3 Medium EPSS 1.0% KEV · Not listed
Vendors
Products
CVE-2025-31140

In JetBrains TeamCity before 2025.03 stored XSS was possible on Cloud Profiles page

CVSS 3.1 · 4.6 Medium EPSS 28.0% KEV · Not listed
Vendors
Products
CVE-2025-31141

In JetBrains TeamCity before 2025.03 exception could lead to credential leakage on Cloud Profiles page

CVSS 3.1 · 2.7 Low EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-46432

In JetBrains TeamCity before 2025.03.1 base64-encoded credentials could be exposed in build logs

CVSS 3.1 · 4.3 Medium EPSS 1.0% KEV · Not listed
Vendors
Products
CVE-2025-46433

In JetBrains TeamCity before 2025.03.1 improper path validation in loggingPreset parameter was possible

CVSS 3.1 · 4.9 Medium EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-46618

In JetBrains TeamCity before 2025.03.1 stored XSS was possible on Data Directory tab

CVSS 3.1 · 3.5 Low EPSS 63.0% KEV · Not listed
Vendors
Products
CVE-2024-26152

Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config

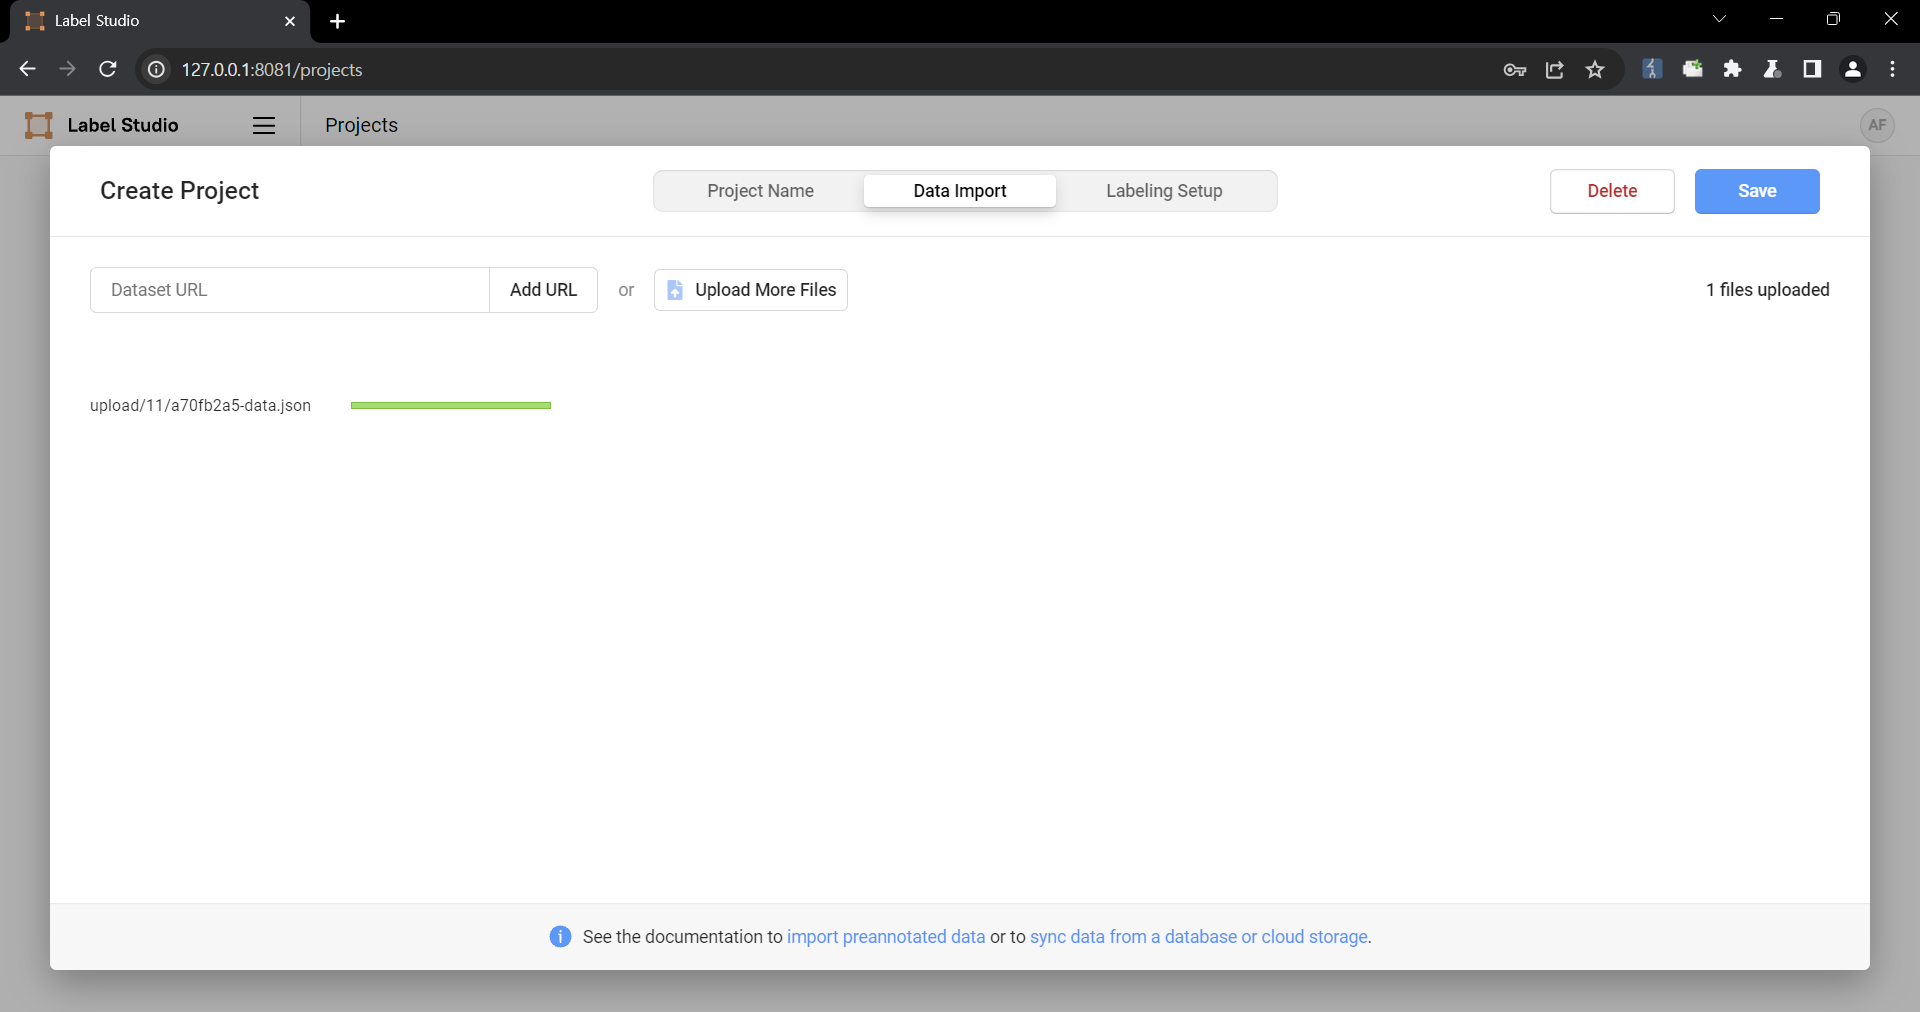
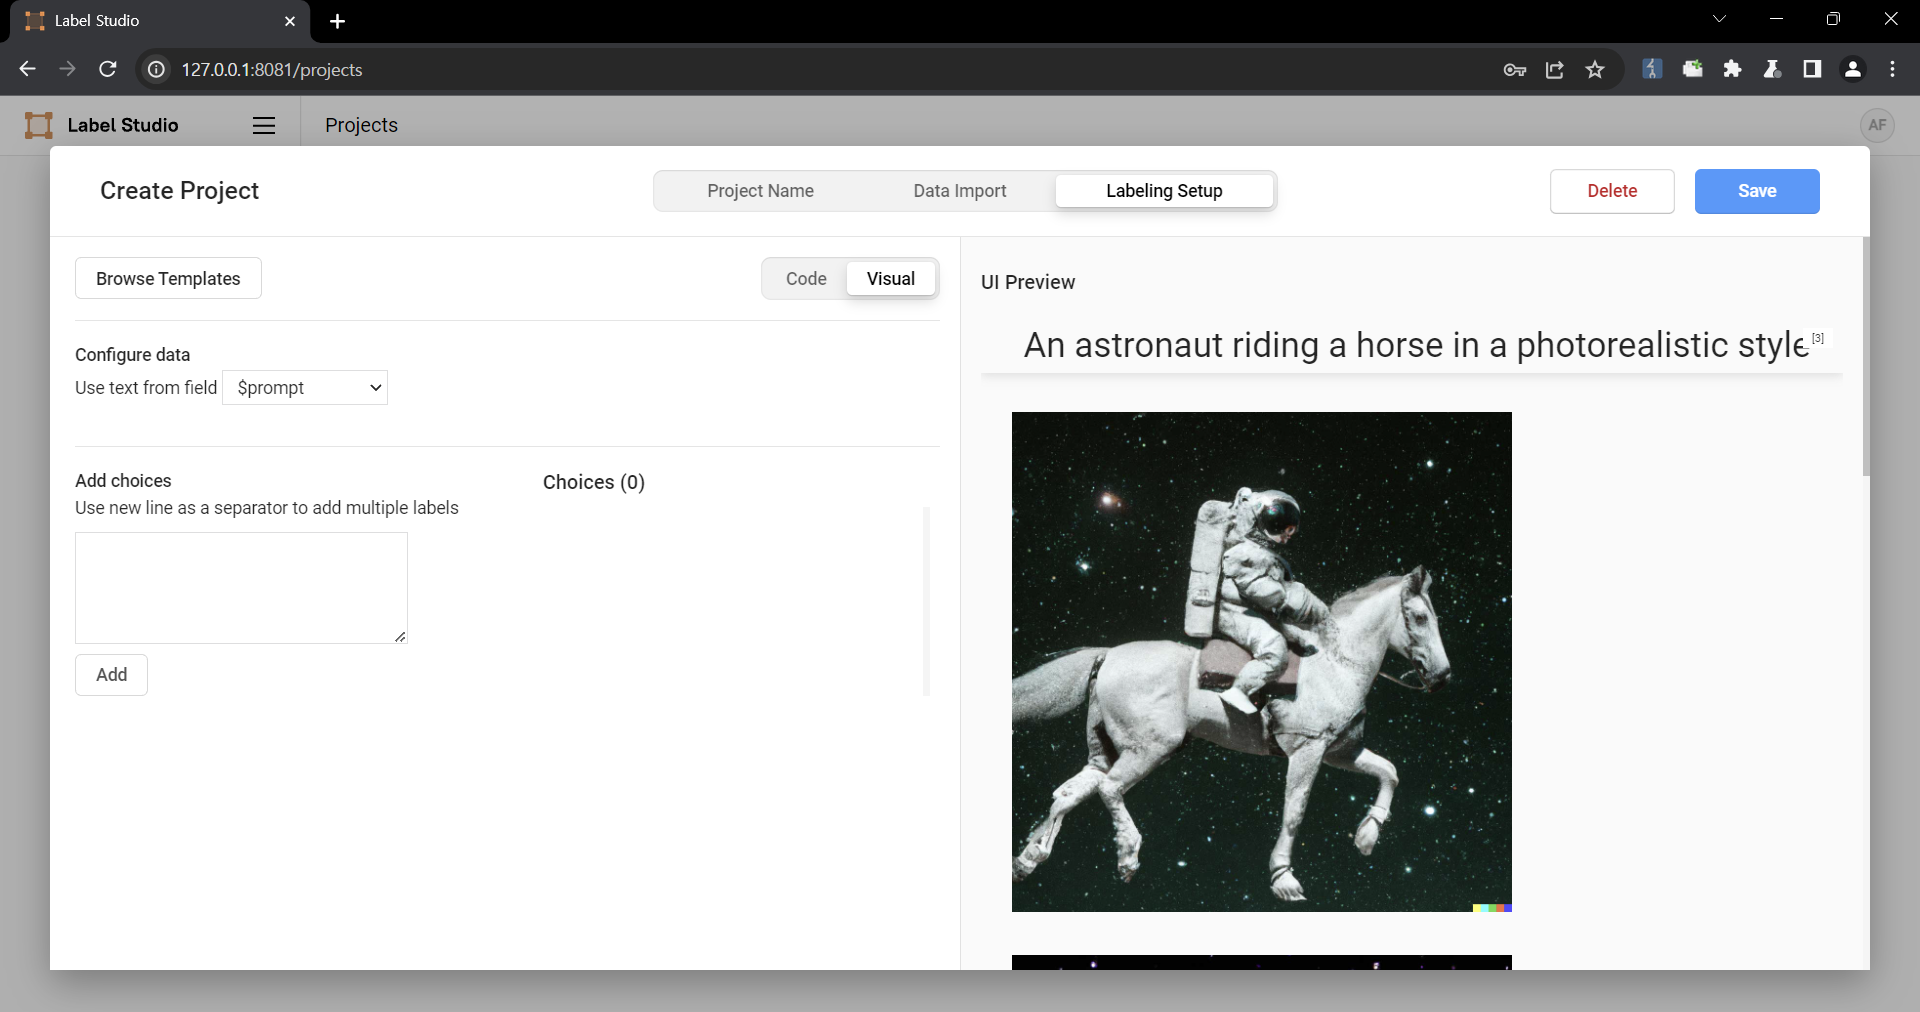
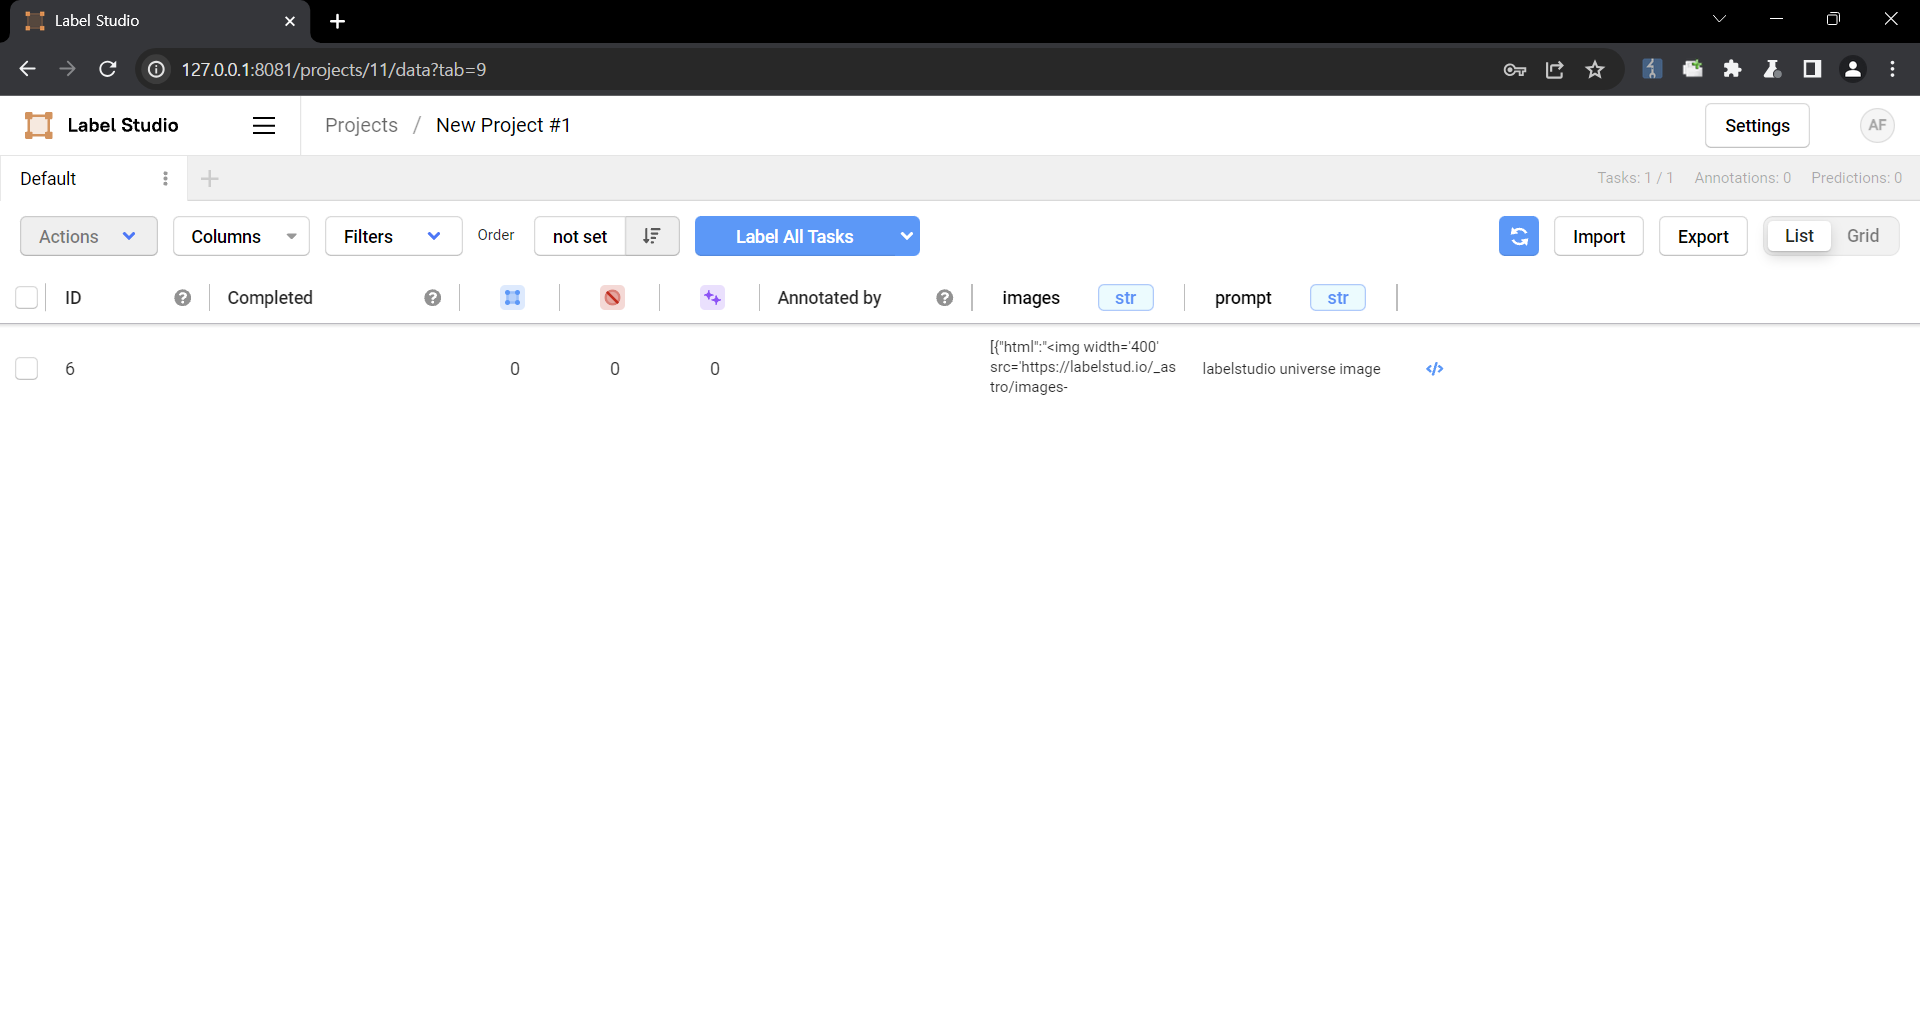
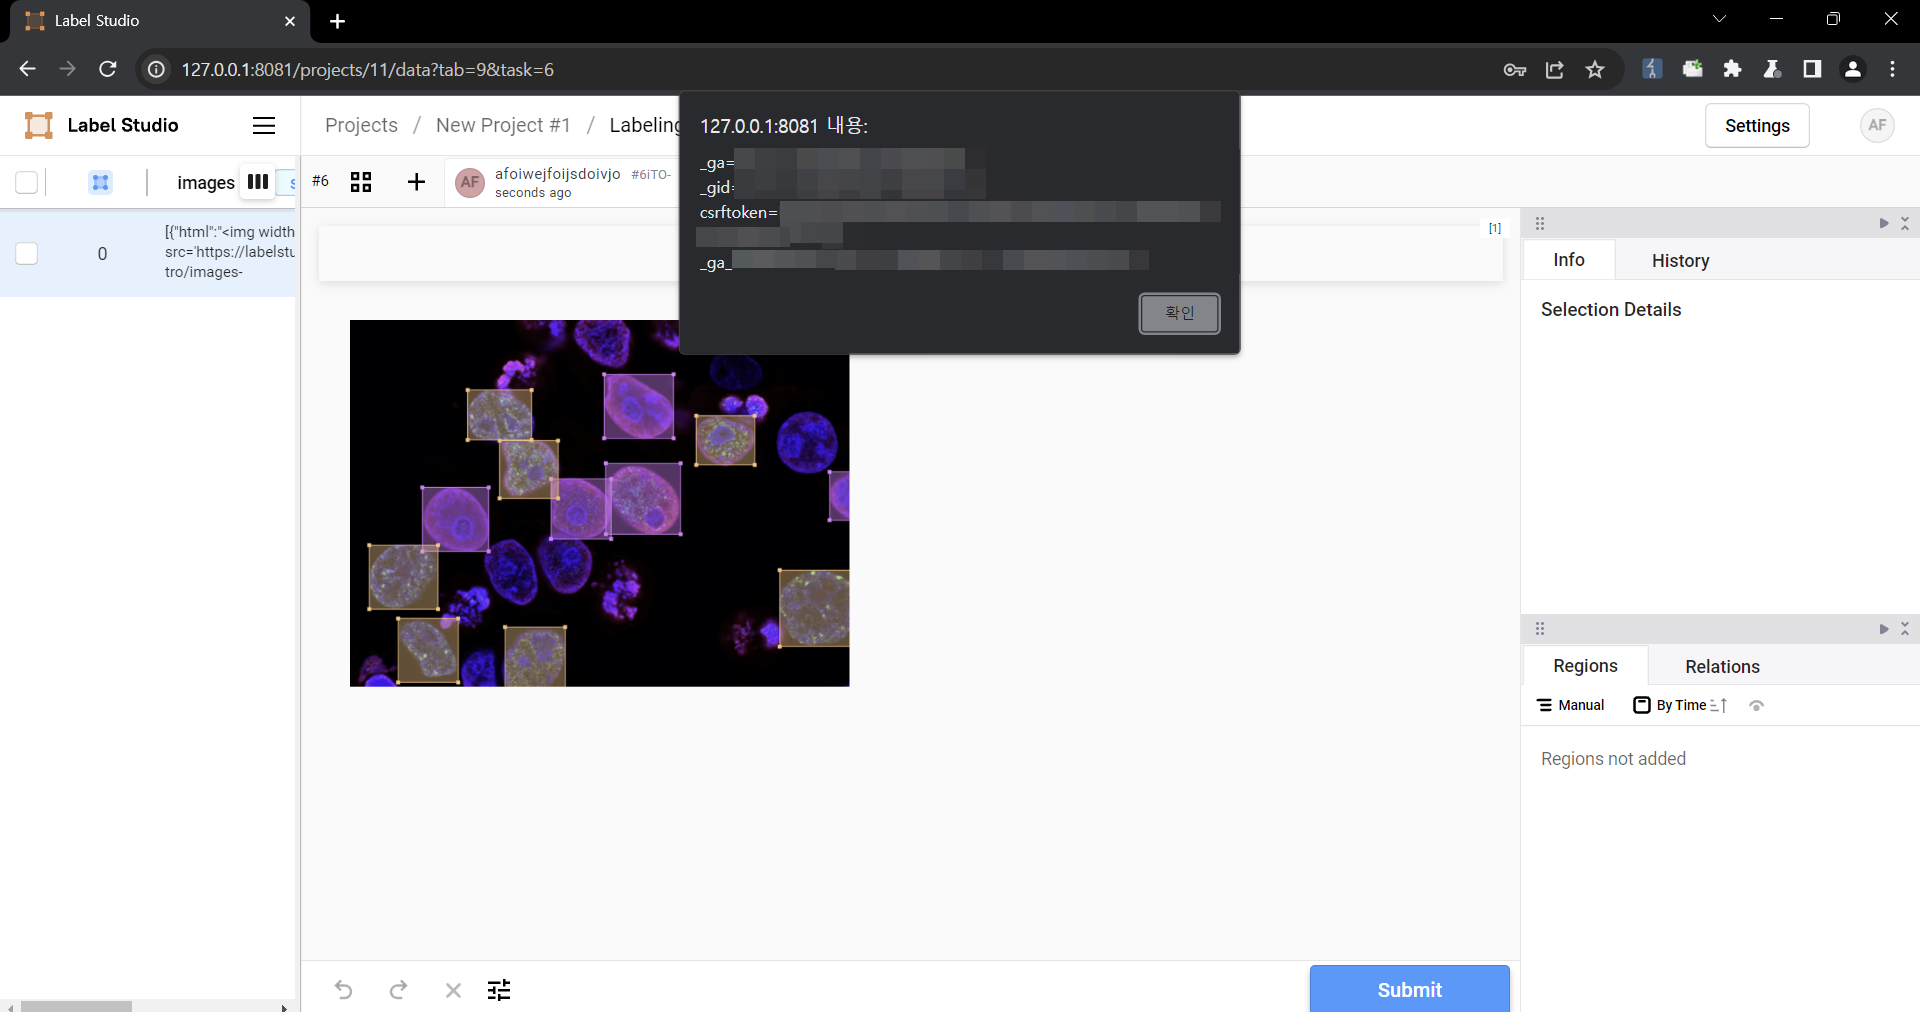
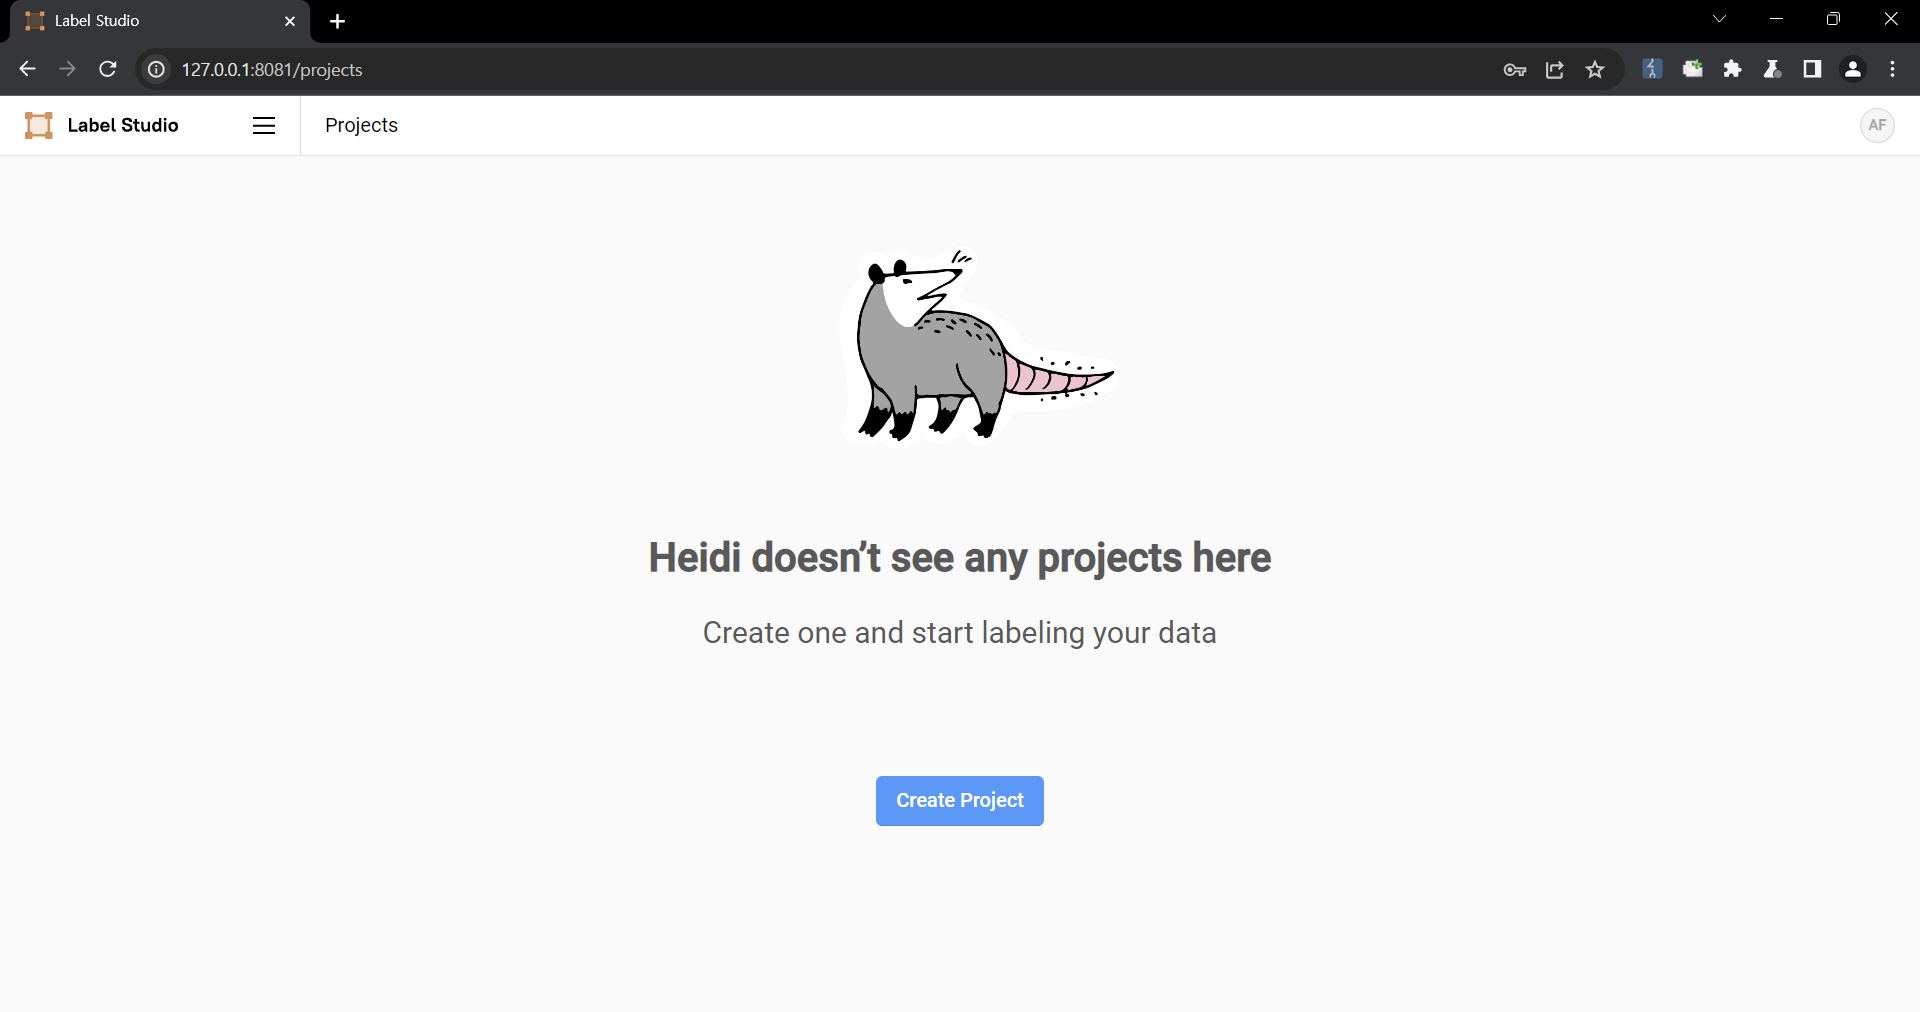
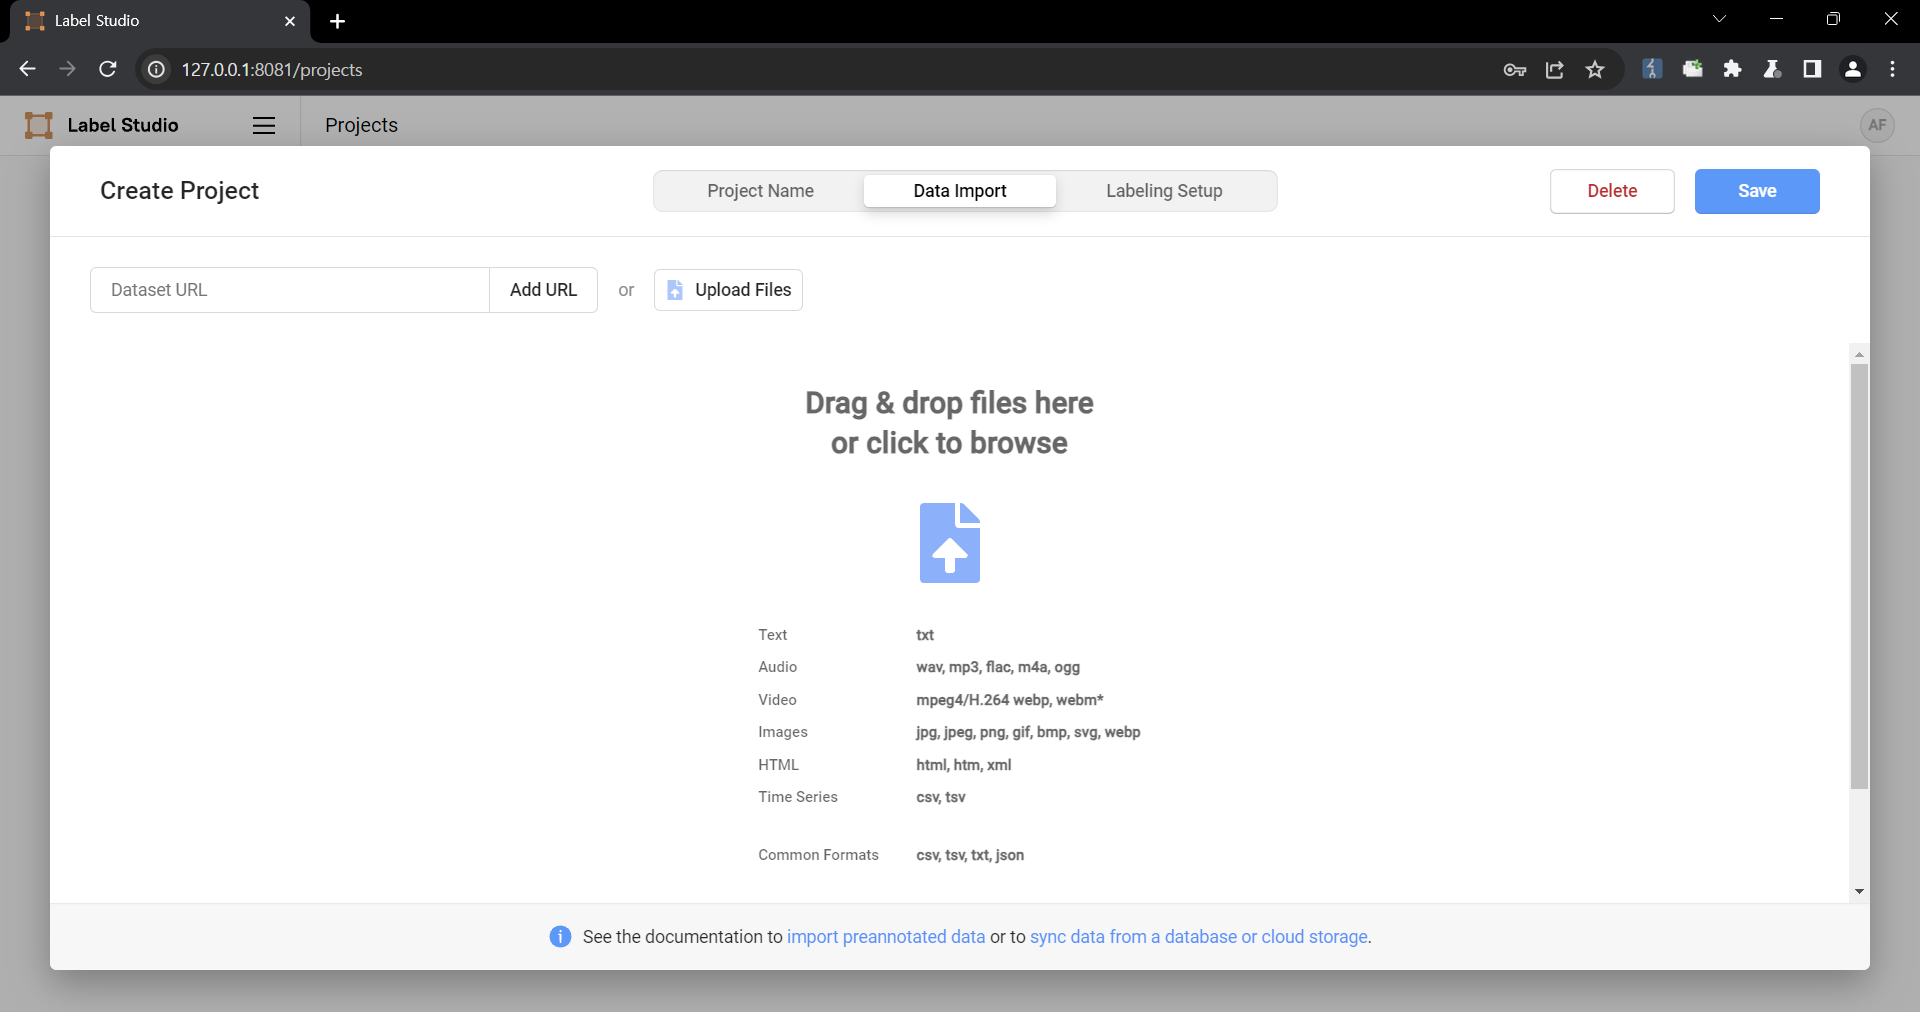
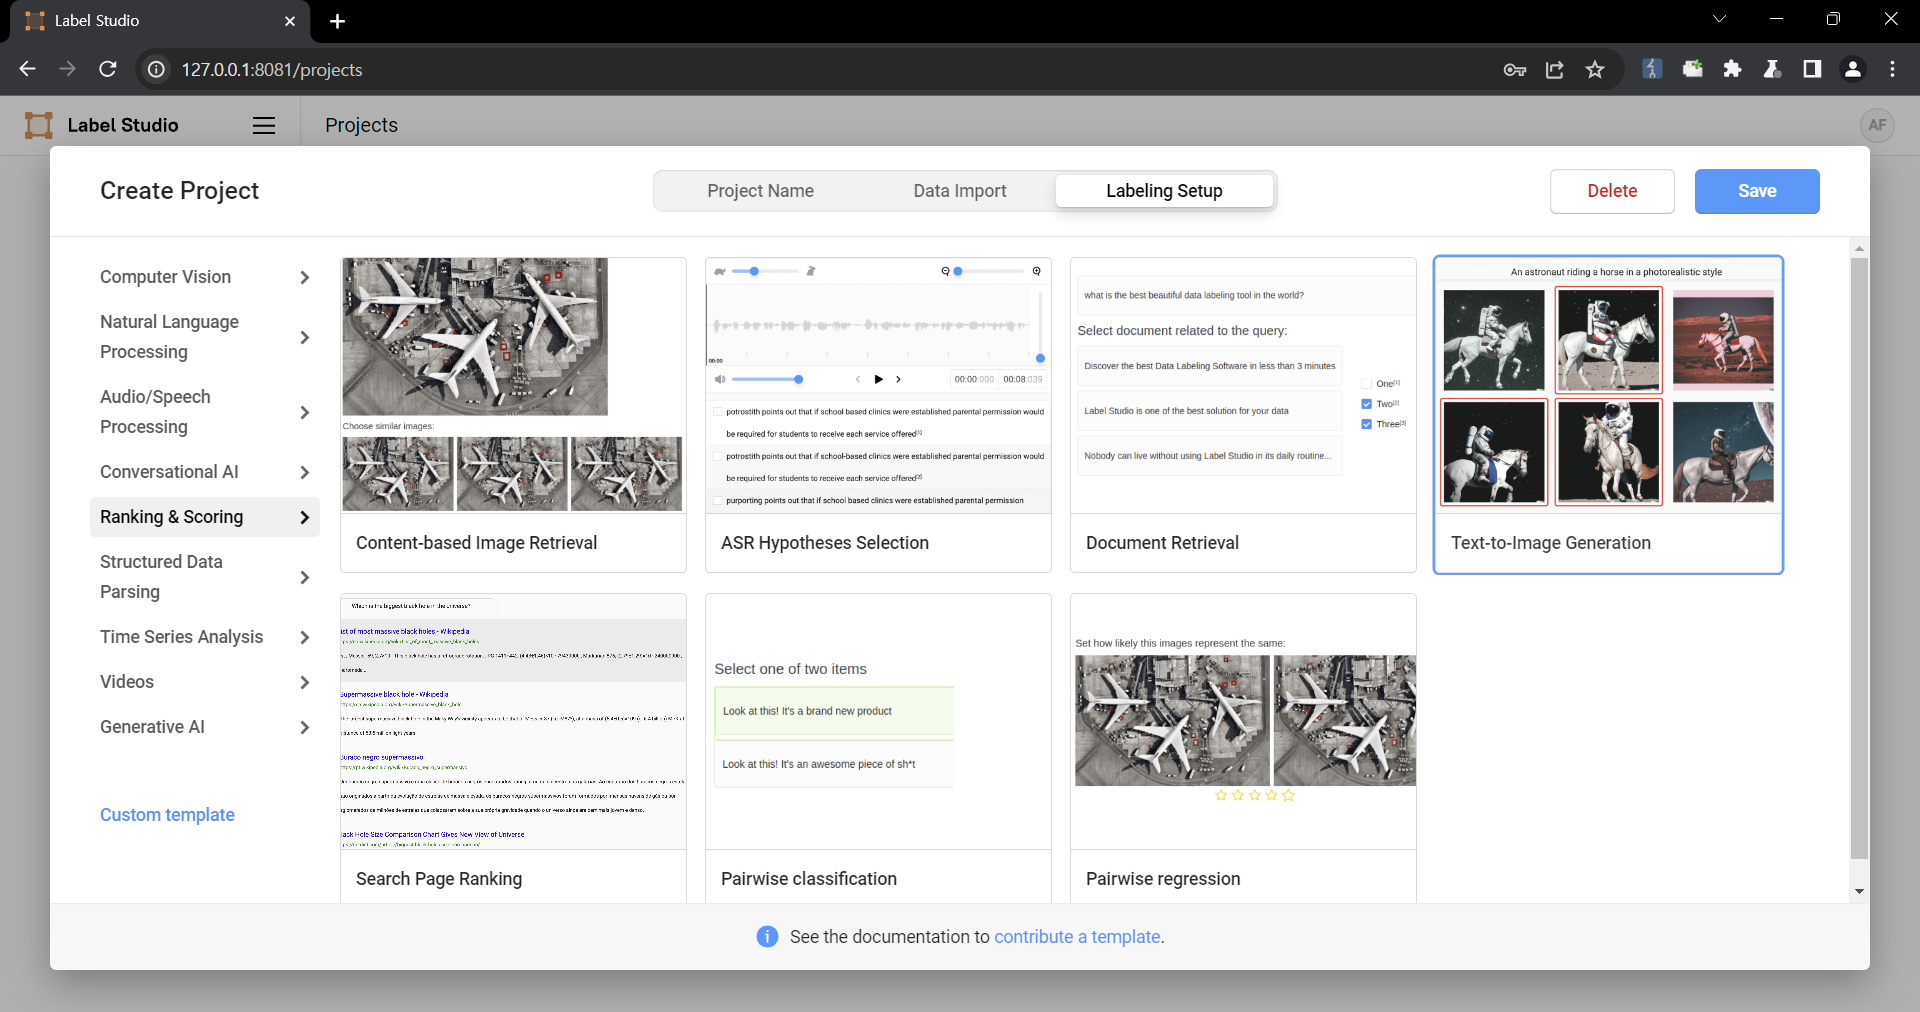
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. ![Create a project](https://github.com/HumanSignal/label-studio/assets/3943358/9b1536ad-feac-4238-a1bd-ca9b1b798673) 2. Upload a file containing the payload using the "Upload Files" function. ![2 Upload a file containing the payload using the Upload Files function](https://github.com/HumanSignal/label-studio/assets/3943358/26bb7af1-1cd2-408f-9adf-61e31a5b7328) ![3 complete](https://github.com/HumanSignal/label-studio/assets/3943358/f2f62774-1fa6-4456-9e6f-8fa1ca0a2d2e) The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring ![3 Select the text-to-image generation labelling template for Ranking and scoring](https://github.com/HumanSignal/label-studio/assets/3943358/f227f49c-a718-4738-bc2a-807da4f97155) ![5 save](https://github.com/HumanSignal/label-studio/assets/3943358/9b529f8a-8e99-4bb0-bdf6-bb7a95c9b75d) 4. Select a task ![4 Select a task](https://github.com/HumanSignal/label-studio/assets/3943358/71856b7a-2b1f-44ea-99ab-fc48bc20caa7) 5. Check that the script is running ![5 Check that the script is running](https://github.com/HumanSignal/label-studio/assets/3943358/e396ae7b-a591-4db7-afe9-5bab30b48cb9) ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
CVSS 3.1 · 4.7 Medium EPSS 2.2% KEV · Not listed
Vendors
Products
CVE-2023-3966

Openvswsitch: ovs-vswitch fails to recover after malformed geneve metadata packet

A flaw was found in Open vSwitch where multiple versions are vulnerable to crafted Geneve packets, which may result in a denial of service and invalid memory accesses. Triggering this issue requires that hardware offloading via the netlink path is enabled.

CVSS 3.1 · 7.5 High EPSS 1.3% KEV · Not listed
Products