Search vulnerabilities

Results 429,927

CVE-2025-26493

In JetBrains TeamCity before 2024.12.2 several DOM-based XSS were possible on the Code Inspection Report tab

CVSS 3.1 · 4.6 Medium EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-31139

In JetBrains TeamCity before 2025.03 base64 encoded password could be exposed in build log

CVSS 3.1 · 4.3 Medium EPSS 1.0% KEV · Not listed
Vendors
Products
CVE-2025-31140

In JetBrains TeamCity before 2025.03 stored XSS was possible on Cloud Profiles page

CVSS 3.1 · 4.6 Medium EPSS 28.0% KEV · Not listed
Vendors
Products
CVE-2025-31141

In JetBrains TeamCity before 2025.03 exception could lead to credential leakage on Cloud Profiles page

CVSS 3.1 · 2.7 Low EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-46432

In JetBrains TeamCity before 2025.03.1 base64-encoded credentials could be exposed in build logs

CVSS 3.1 · 4.3 Medium EPSS 1.0% KEV · Not listed
Vendors
Products
CVE-2025-46433

In JetBrains TeamCity before 2025.03.1 improper path validation in loggingPreset parameter was possible

CVSS 3.1 · 4.9 Medium EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2025-46618

In JetBrains TeamCity before 2025.03.1 stored XSS was possible on Data Directory tab

CVSS 3.1 · 3.5 Low EPSS 63.0% KEV · Not listed
Vendors
Products
CVE-2024-26152

Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config

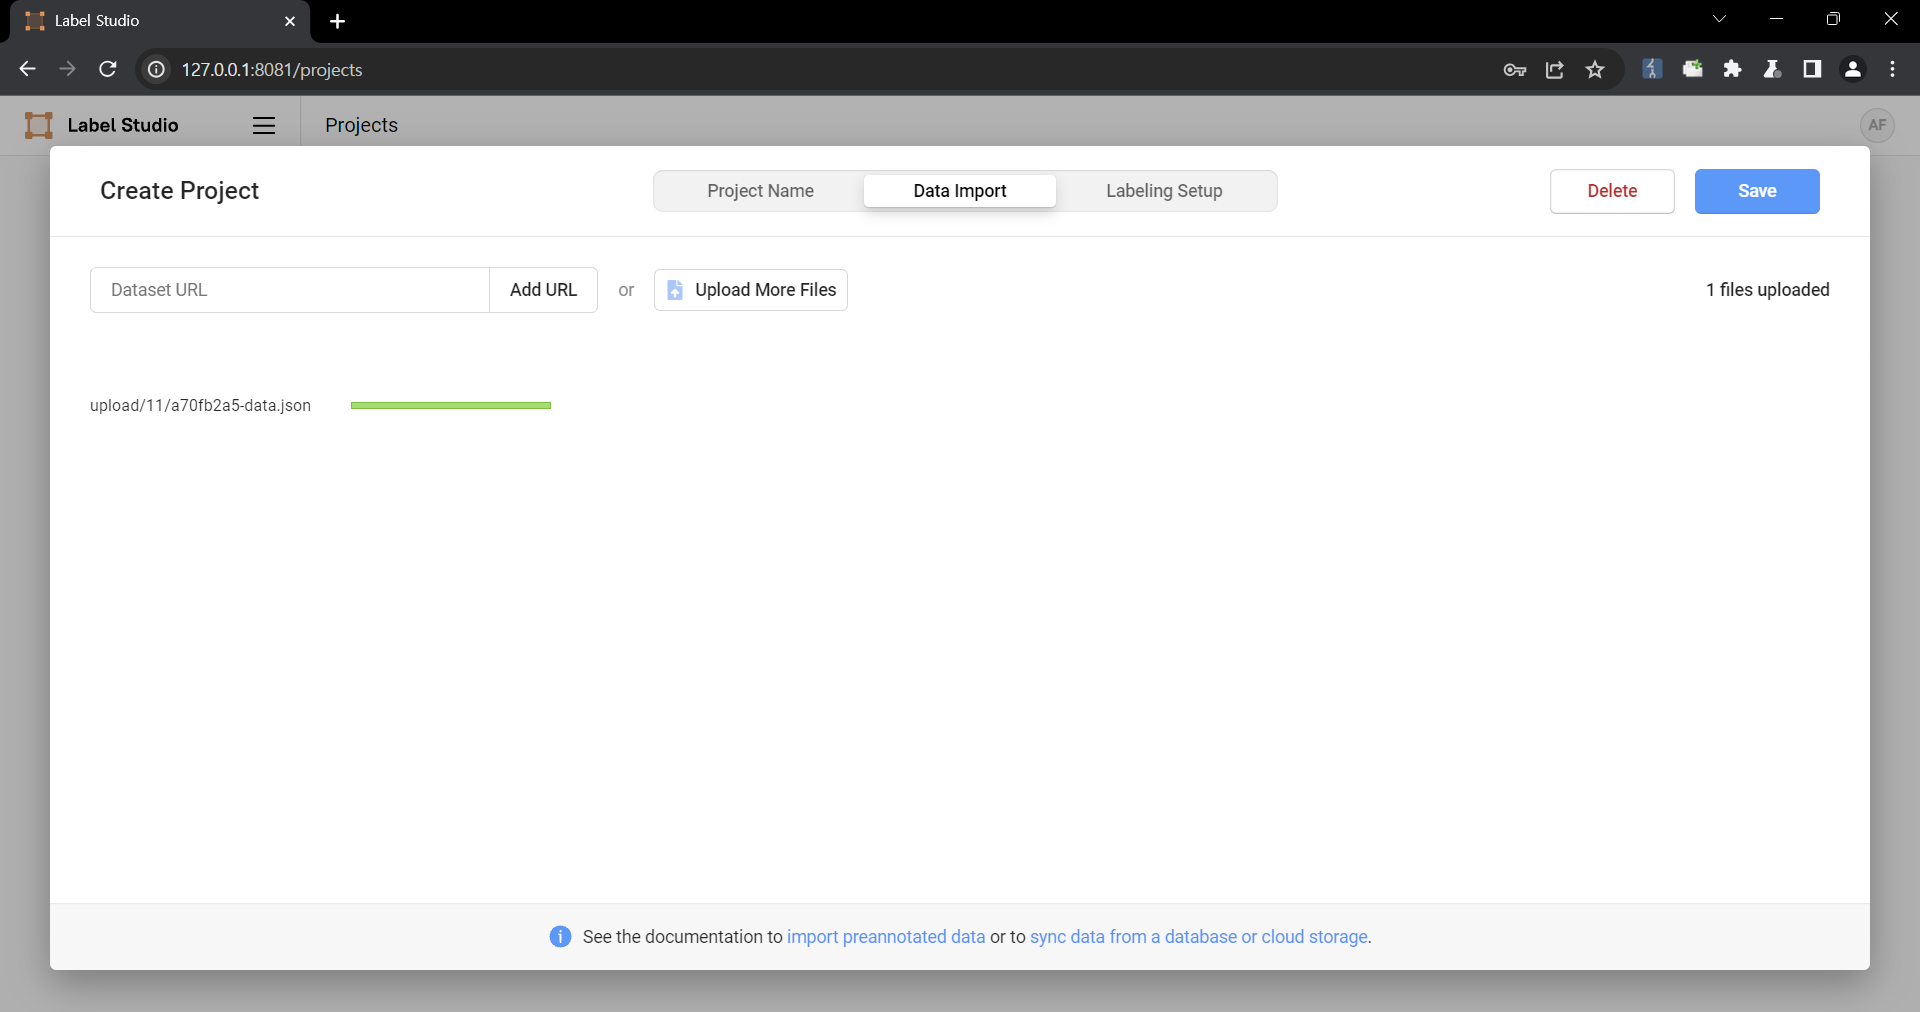
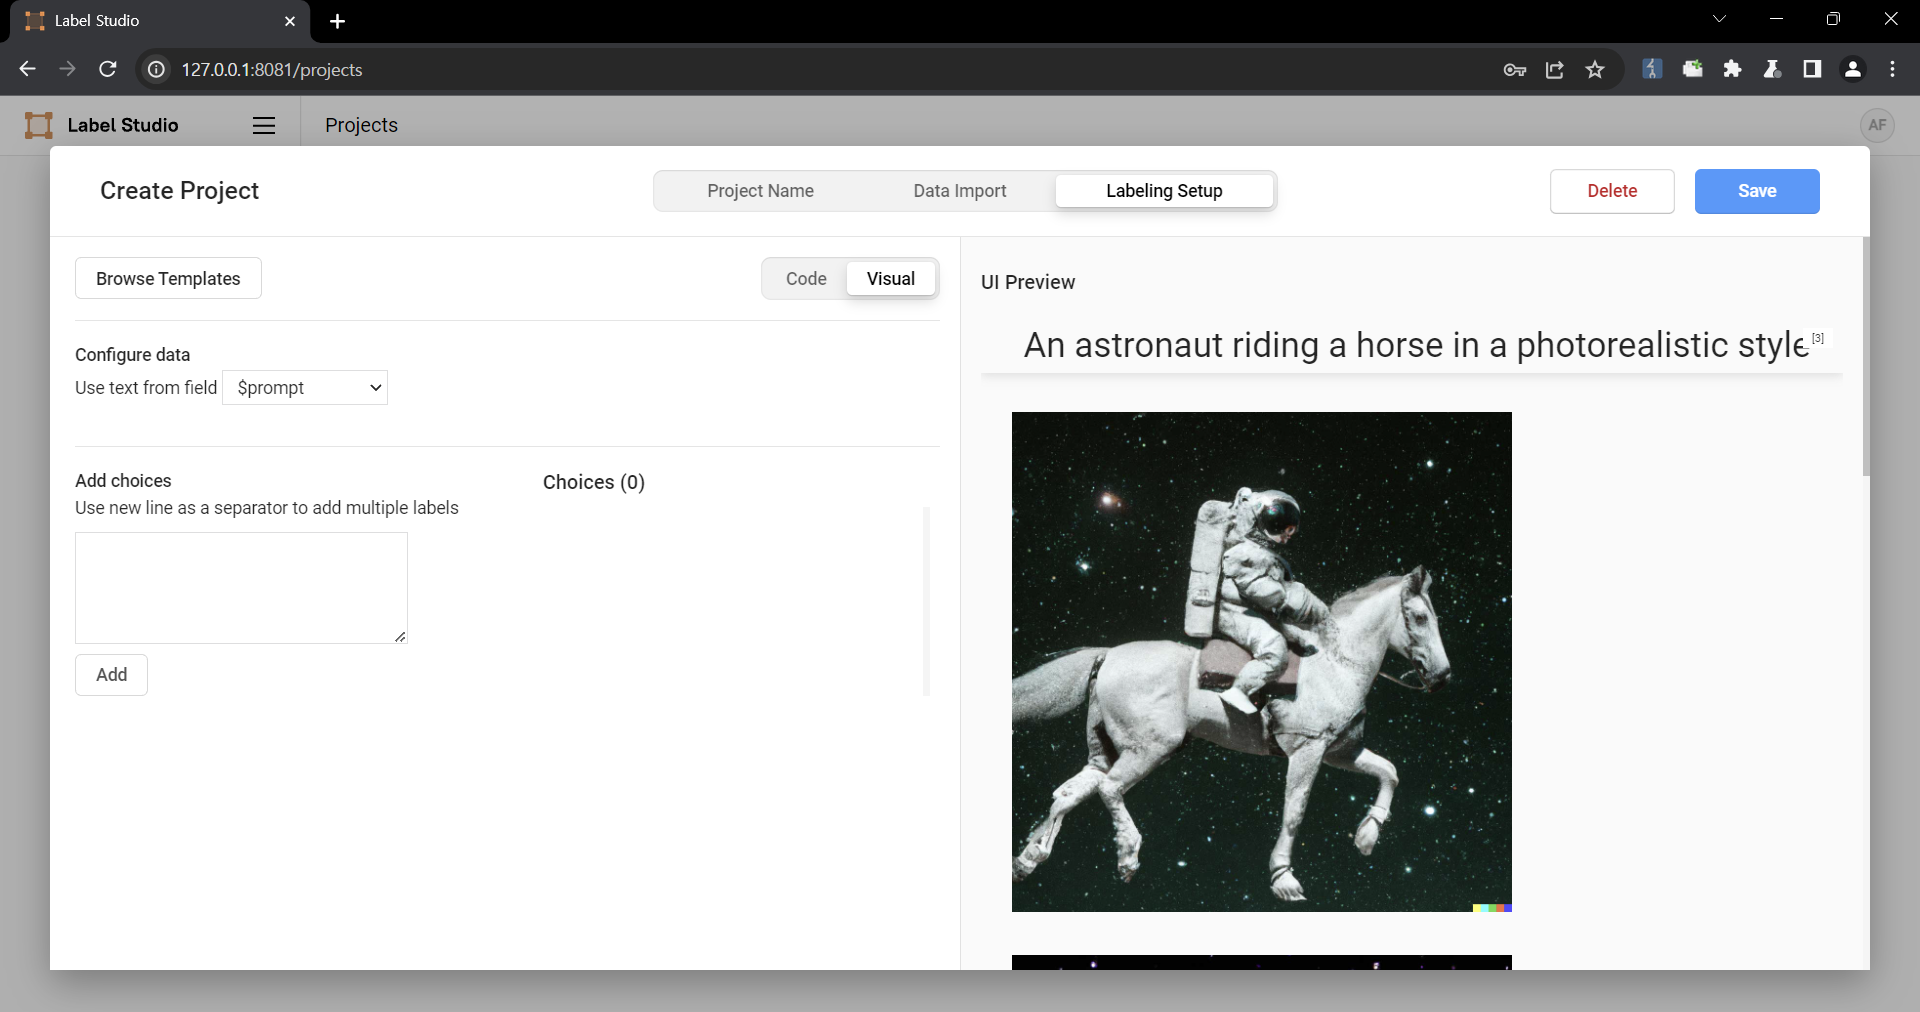
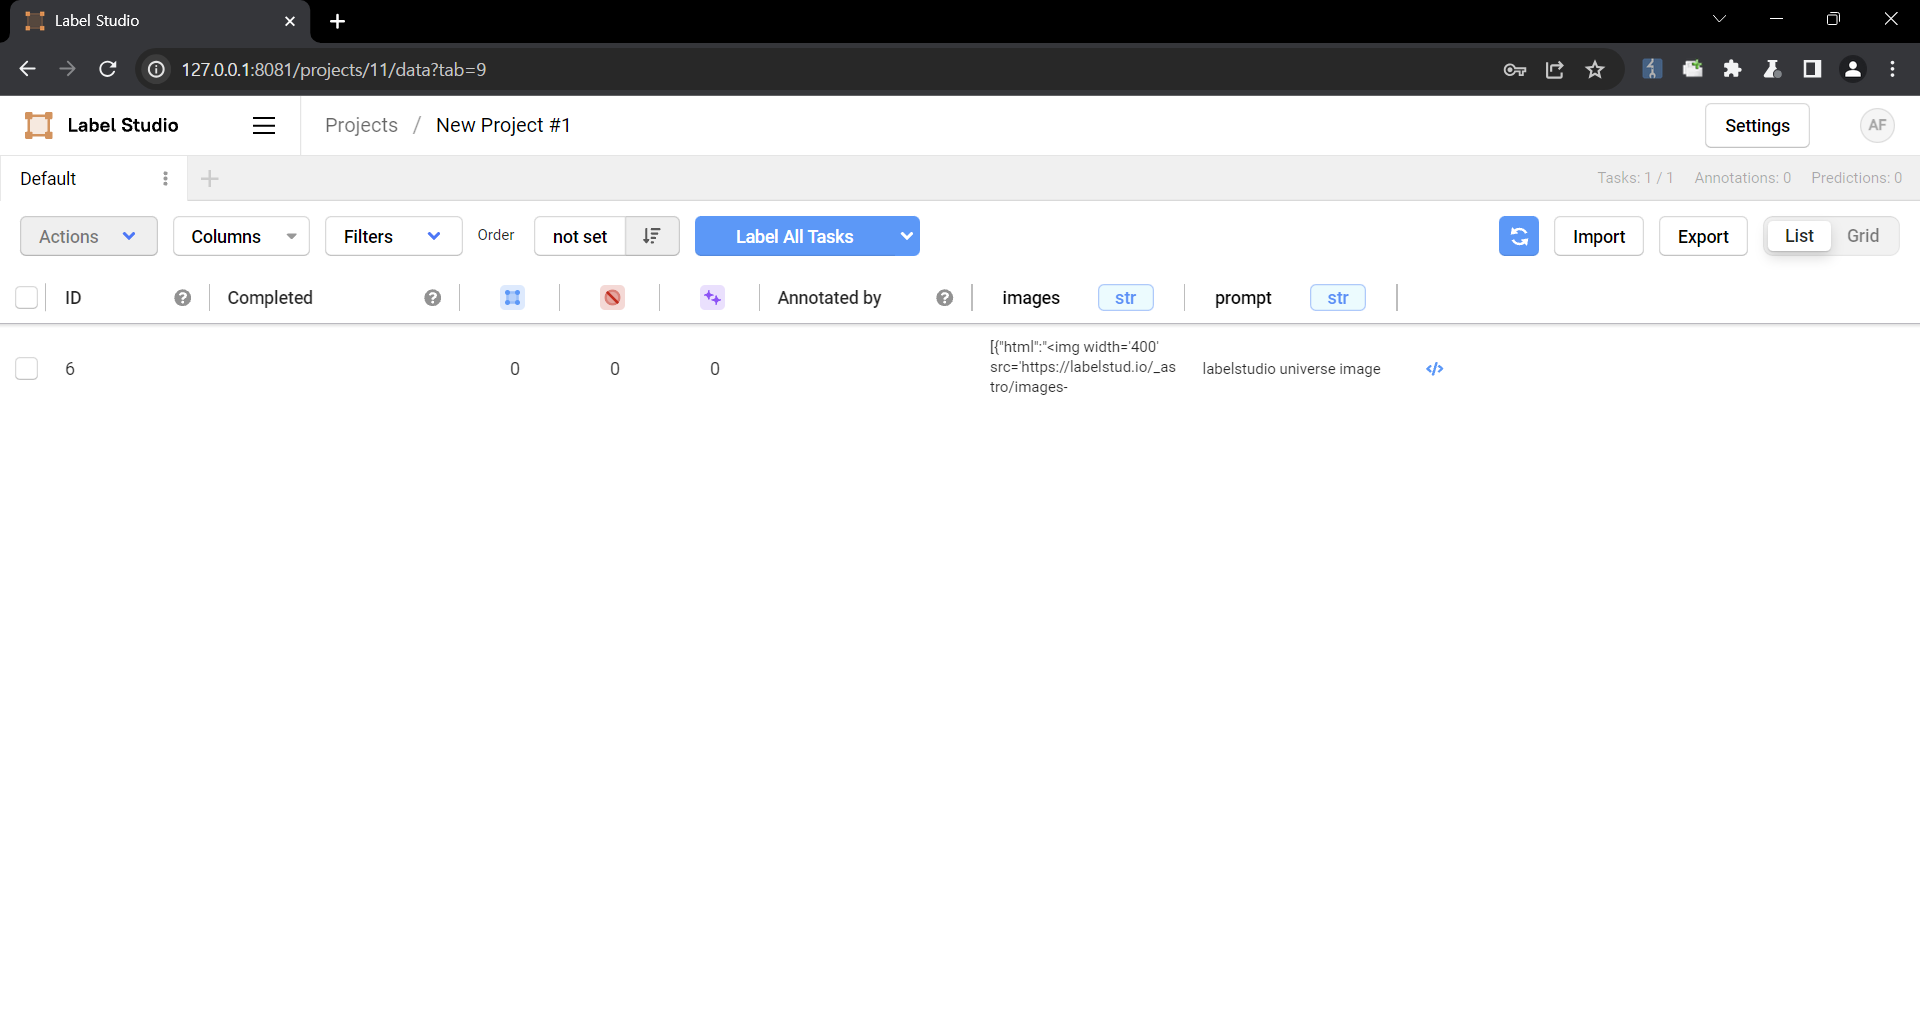
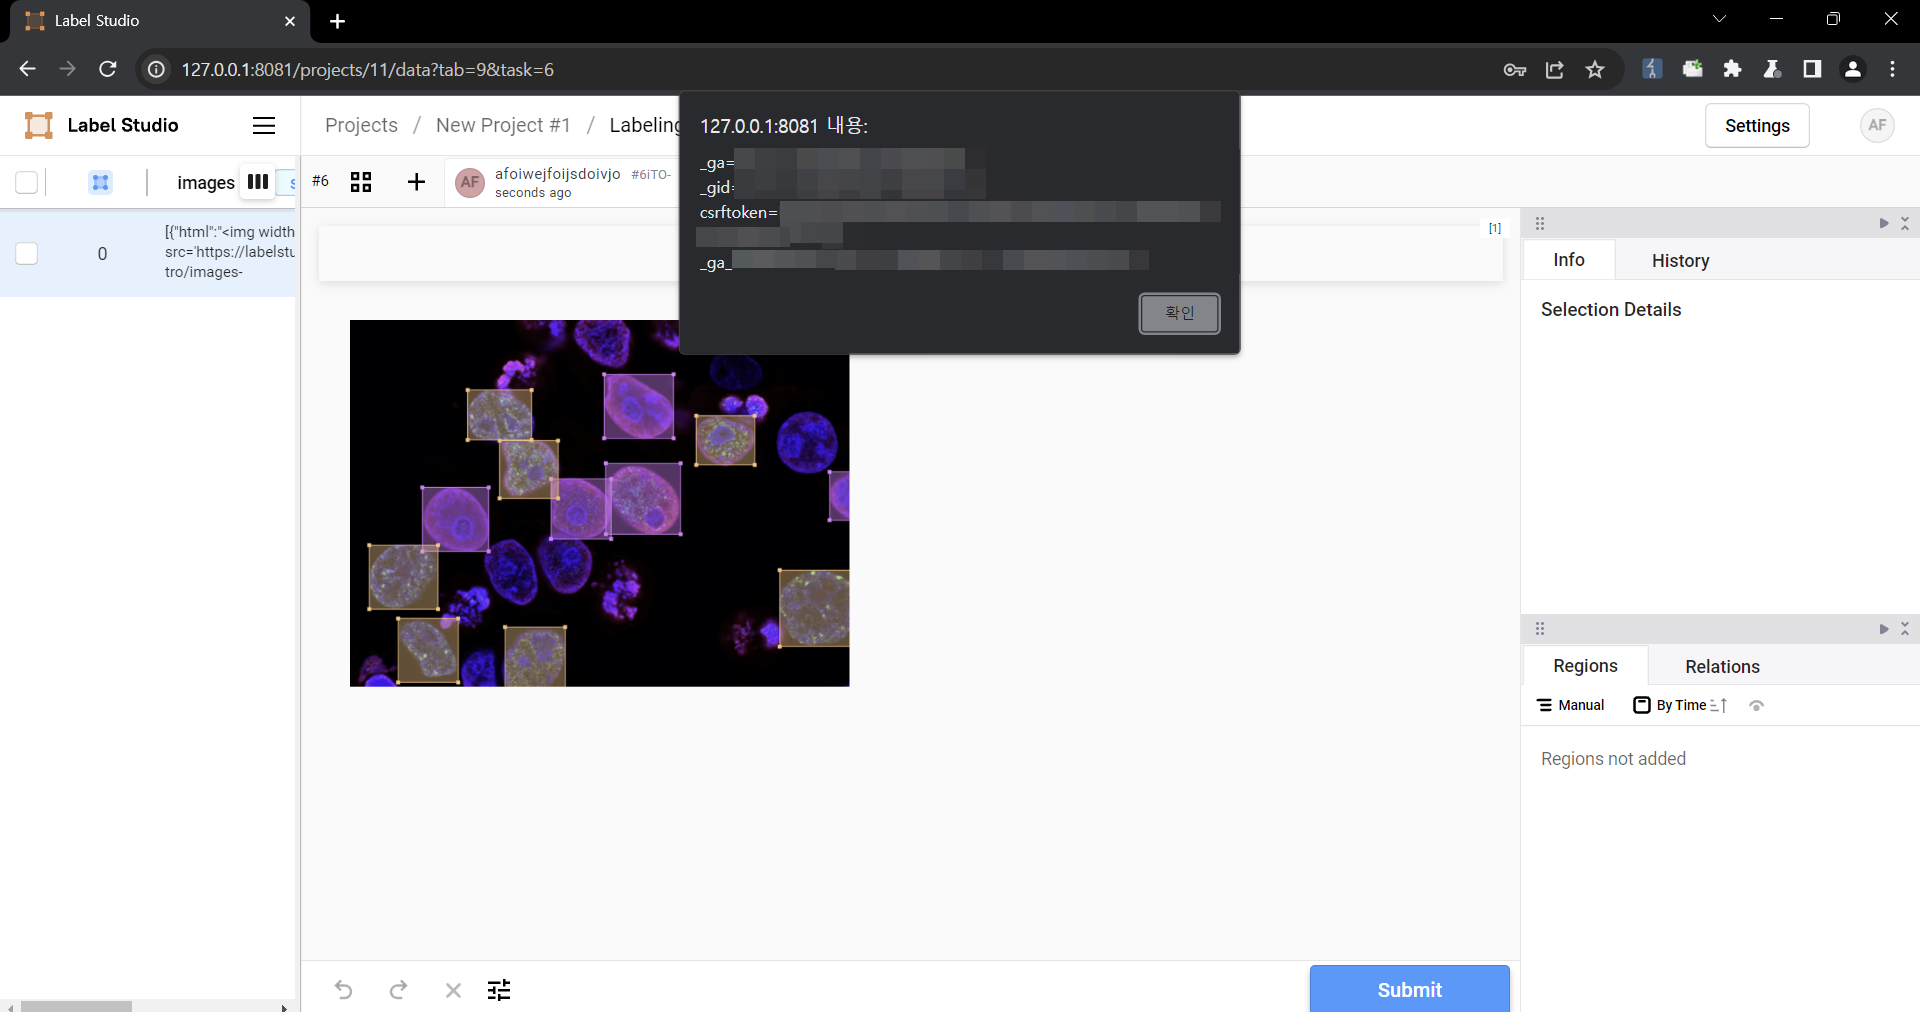
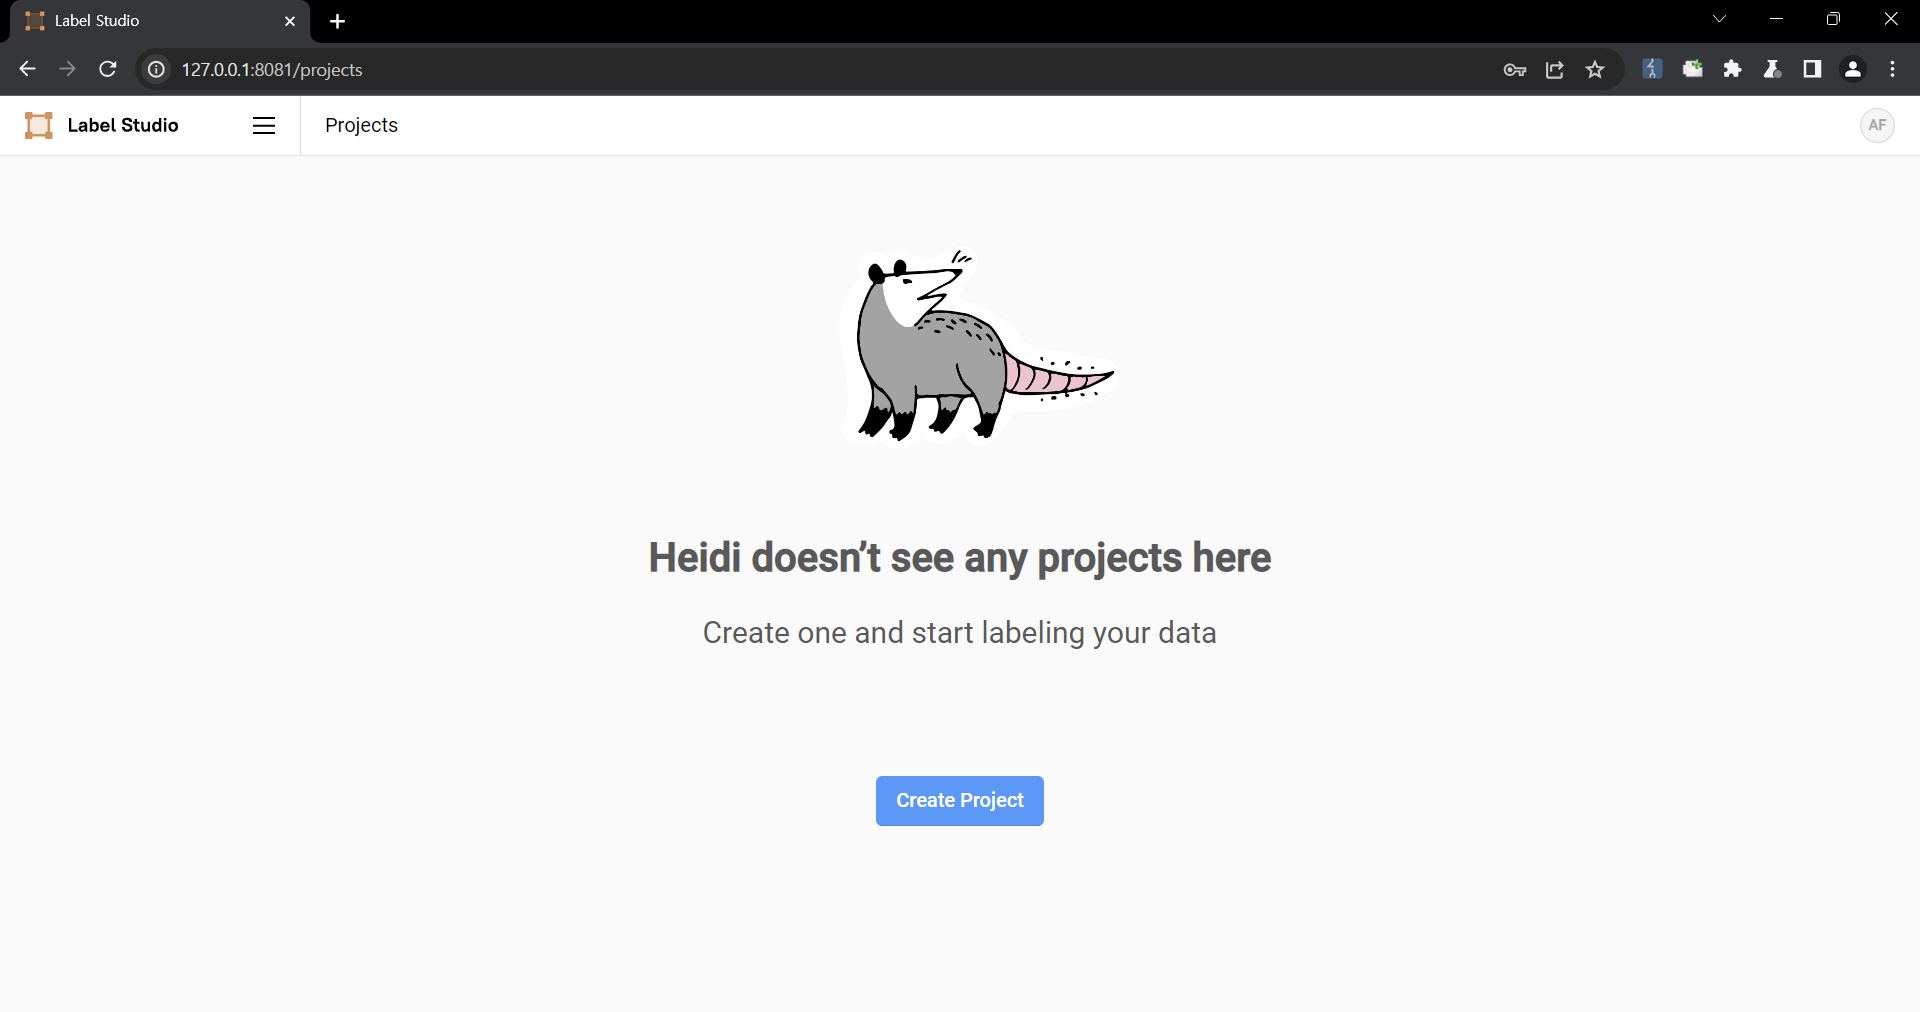
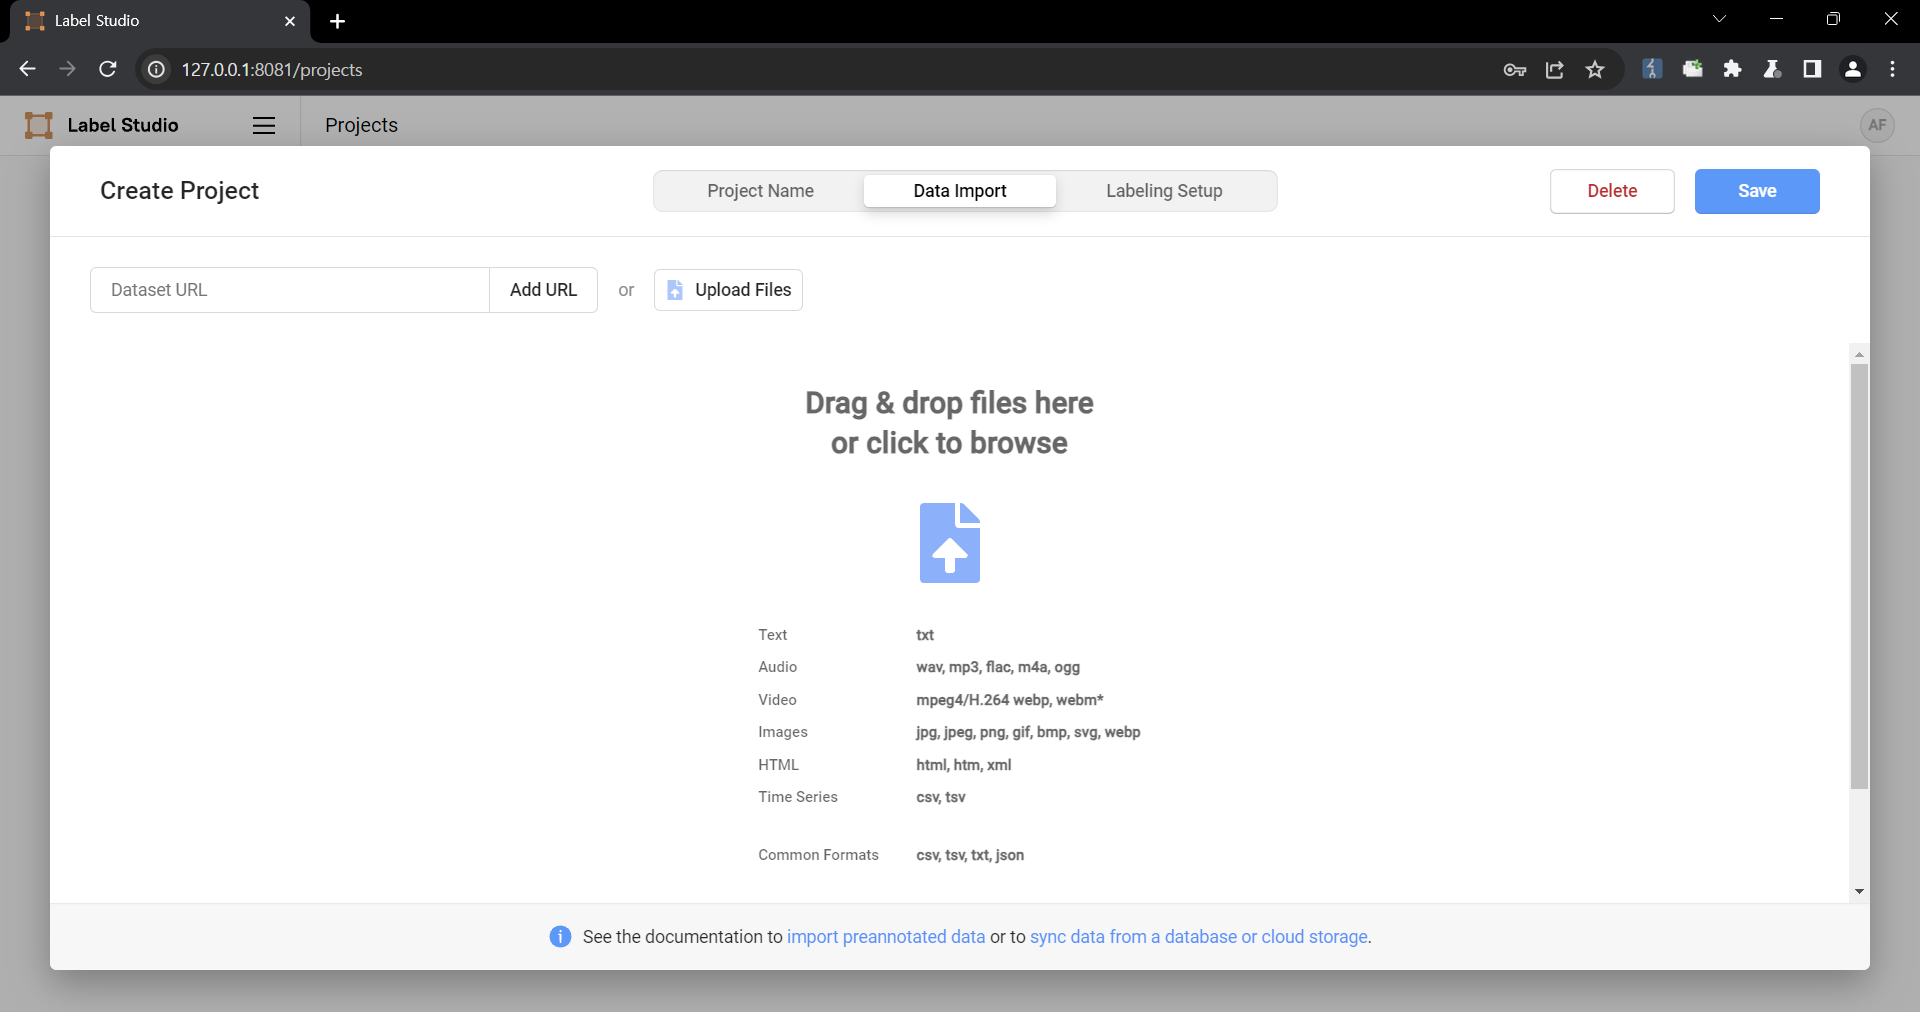
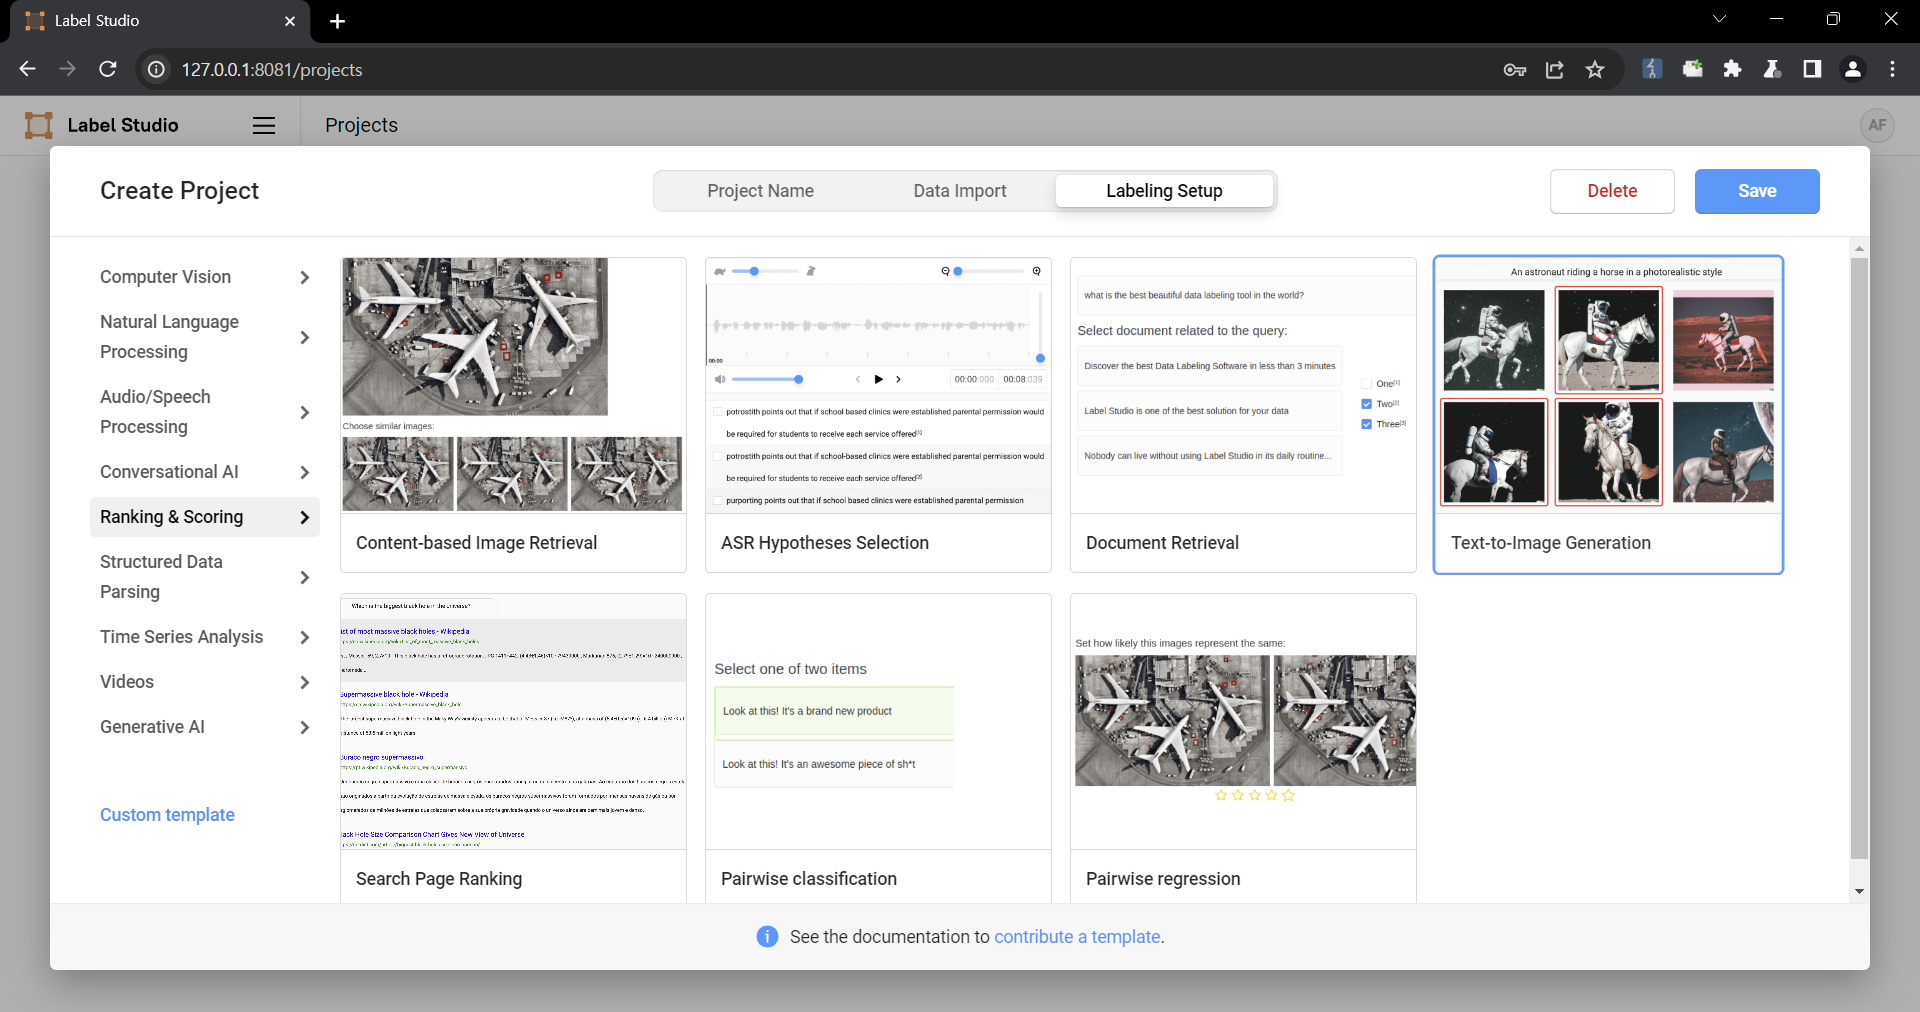
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. ![Create a project](https://github.com/HumanSignal/label-studio/assets/3943358/9b1536ad-feac-4238-a1bd-ca9b1b798673) 2. Upload a file containing the payload using the "Upload Files" function. ![2 Upload a file containing the payload using the Upload Files function](https://github.com/HumanSignal/label-studio/assets/3943358/26bb7af1-1cd2-408f-9adf-61e31a5b7328) ![3 complete](https://github.com/HumanSignal/label-studio/assets/3943358/f2f62774-1fa6-4456-9e6f-8fa1ca0a2d2e) The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring ![3 Select the text-to-image generation labelling template for Ranking and scoring](https://github.com/HumanSignal/label-studio/assets/3943358/f227f49c-a718-4738-bc2a-807da4f97155) ![5 save](https://github.com/HumanSignal/label-studio/assets/3943358/9b529f8a-8e99-4bb0-bdf6-bb7a95c9b75d) 4. Select a task ![4 Select a task](https://github.com/HumanSignal/label-studio/assets/3943358/71856b7a-2b1f-44ea-99ab-fc48bc20caa7) 5. Check that the script is running ![5 Check that the script is running](https://github.com/HumanSignal/label-studio/assets/3943358/e396ae7b-a591-4db7-afe9-5bab30b48cb9) ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
CVSS 3.1 · 4.7 Medium EPSS 2.2% KEV · Not listed
Vendors
Products
CVE-2023-3966

Openvswsitch: ovs-vswitch fails to recover after malformed geneve metadata packet

A flaw was found in Open vSwitch where multiple versions are vulnerable to crafted Geneve packets, which may result in a denial of service and invalid memory accesses. Triggering this issue requires that hardware offloading via the netlink path is enabled.

CVSS 3.1 · 7.5 High EPSS 1.3% KEV · Not listed
Products
CVE-2025-4500

code-projects Hotel Management System Edit Room edit stack-based overflow

A vulnerability, which was classified as critical, has been found in code-projects Hotel Management System 1.0. Affected by this issue is the function Edit of the component Edit Room. The manipulation of the argument roomnumber leads to stack-based buffer overflow. An attack has to be approached locally. The exploit has been disclosed to the public and may be used.

CVSS 4.0 · 4.8 Medium EPSS < 1% KEV · Not listed
Vendors
CVE-2022-42160

D-Link COVR 1200,1202,1203 v1.08 was discovered to contain a command injection vulnerability via the system_time_timezone parameter at function SetNTPServerSettings.

CVSS 3.1 · 8.8 High EPSS 2.7% KEV · Not listed
Vendors
Products
CVE-2022-34020

Cross Site Request Forgery (CSRF) vulnerability in ResIOT ResIOT IOT Platform + LoRaWAN Network Server through 4.1.1000114 allows attackers to add new admin users to the platform or other unspecified impacts.

CVSS 3.1 · 8.8 High EPSS < 1% KEV · Not listed
Vendors
CVE-2022-33106

WiJungle NGFW Version U250 was discovered to be vulnerable to No Rate Limit attack, allowing the attacker to brute force the admin password leading to Account Take Over.

CVSS 3.1 · 9.8 Critical EPSS < 1% KEV · Not listed
Vendors
Products
CVE-2022-24697

Apache Kylin prior to 4.0.2 allows command injection when the configuration overwrites function overwrites system parameters

Kylin's cube designer function has a command injection vulnerability when overwriting system parameters in the configuration overwrites menu. RCE can be implemented by closing the single quotation marks around the parameter value of “-- conf=” to inject any operating system command into the command line parameters. This vulnerability affects Kylin 2 version 2.6.5 and earlier, Kylin 3 version 3.1.2 and earlier, and Kylin 4 version 4.0.1 and earlier.

CVSS 3.1 · 9.8 Critical EPSS 84.8% KEV · Not listed
Vendors
Products
CVE-2021-20030

SonicWall GMS is vulnerable to file path manipulation resulting that an unauthenticated attacker can gain access to web directory containing application's binaries and configuration files.

CVSS 3.1 · 7.5 High EPSS < 1% KEV · Not listed
Vendors
CVE-2018-18447

dotPDN Paint.NET before 4.1.2 allows Deserialization of Untrusted Data (issue 2 of 2).

CVSS 3.1 · 9.8 Critical EPSS 1.2% KEV · Not listed
Vendors
Products
CVE-2018-18446

dotPDN Paint.NET before 4.1.2 allows Deserialization of Untrusted Data (issue 1 of 2).

CVSS 3.1 · 9.8 Critical EPSS 1.2% KEV · Not listed
Vendors
Products
CVE-2025-2472

PHPGurukul Apartment Visitors Management System Sign In index.php sql injection

A vulnerability has been found in PHPGurukul Apartment Visitors Management System 1.0 and classified as critical. Affected by this vulnerability is an unknown functionality of the file /index.php of the component Sign In. The manipulation of the argument username leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used.

CVSS 4.0 · 6.9 Medium EPSS < 1% KEV · Not listed
Vendors