
The latest features and improvements of OpenCVE
Subscribe via RSS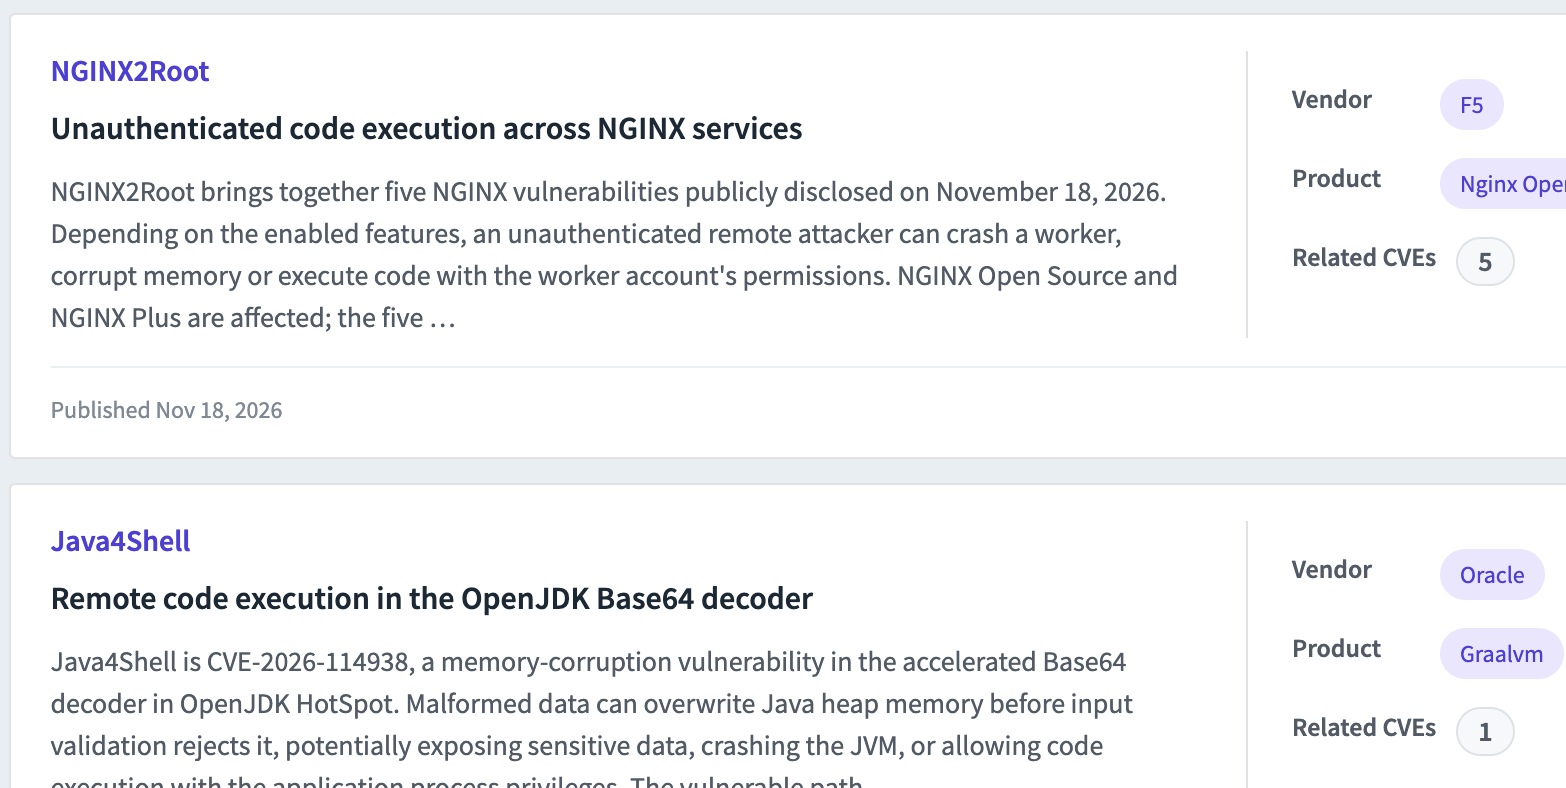
Vulnerability Insights
Nov 19, 2026
Discover Insights, a new section bringing together clear overviews of notable vulnerabilities, related CVEs, and affected technologies.
Find recommended actions, timelines, and original sources for NGINX2Root, Java4Shell, PHP2Shell, and more.
UI Improvements
Nov 13, 2026
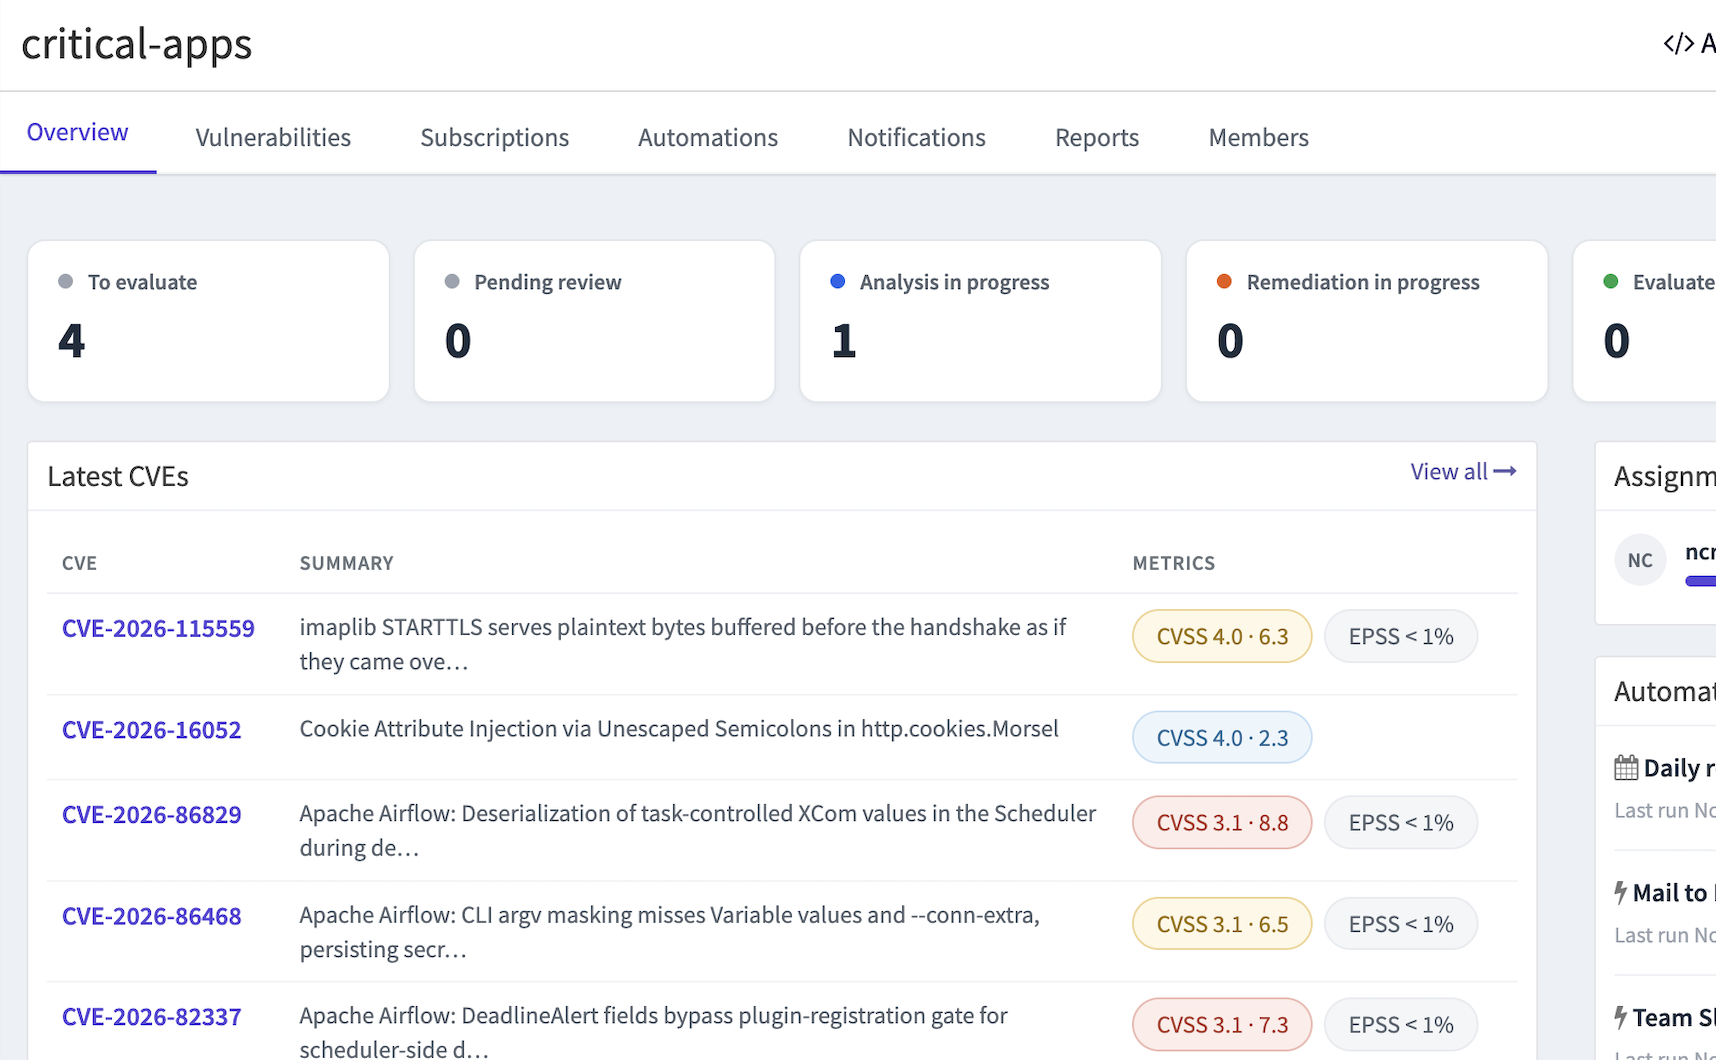
We’ve refreshed OpenCVE with a more modern interface, clearer CVE navigation, and improved project dashboards.
Find CVE details faster and get a better overview of your project’s triage statuses, assignments, and latest vulnerabilities.
Access Control
Aug 13, 2026
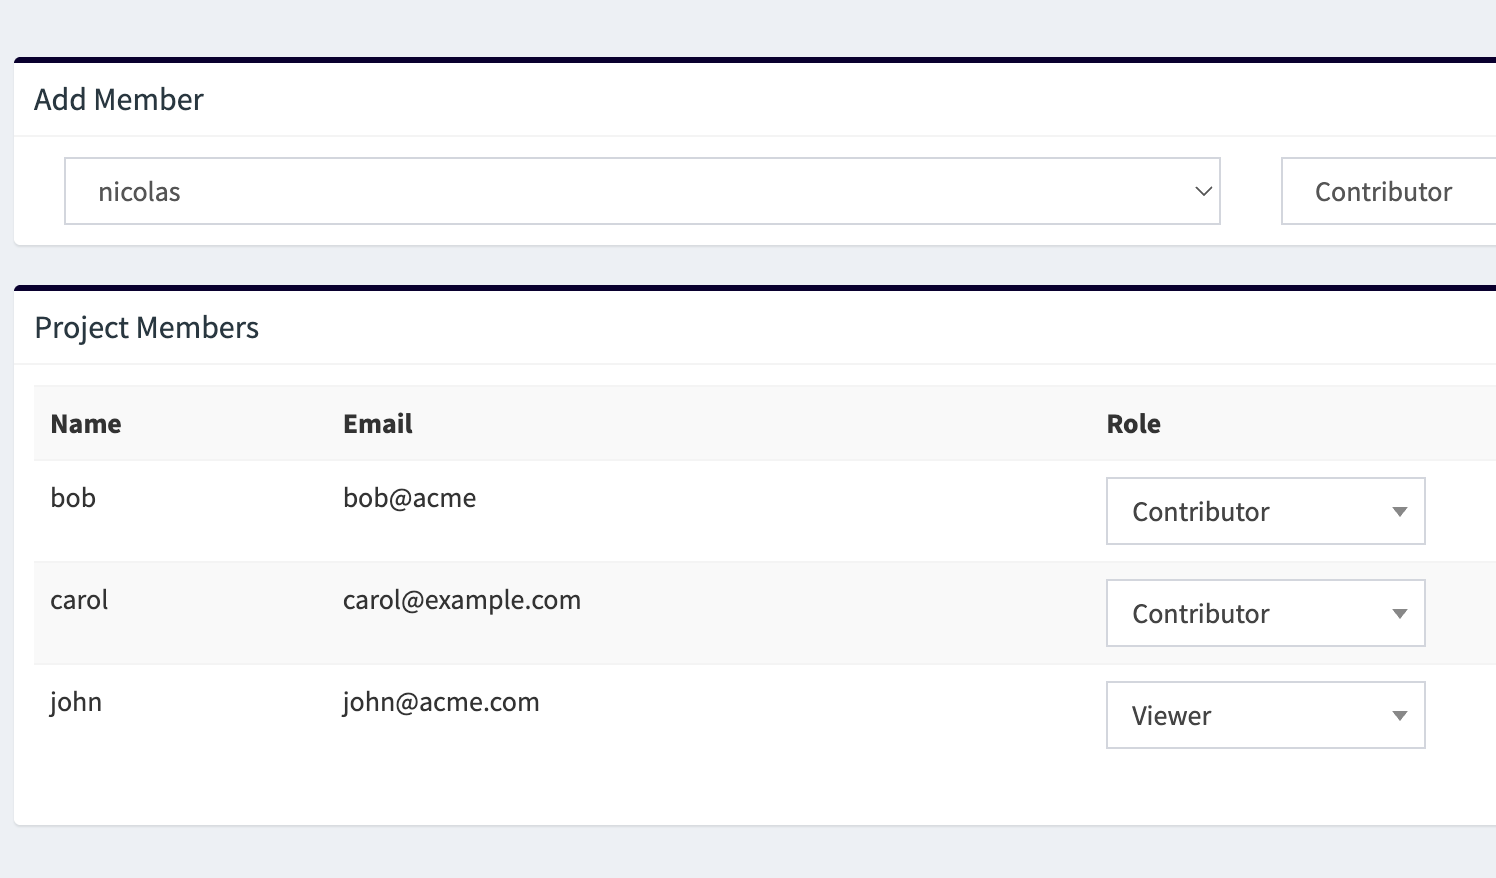
OpenCVE now supports fine-grained access control at the organization and project level.
Assign organization roles to delegate administration, and project roles to give users read-only, triage, or management access only where needed.
OpenCVE API v2
Jul 20, 2026
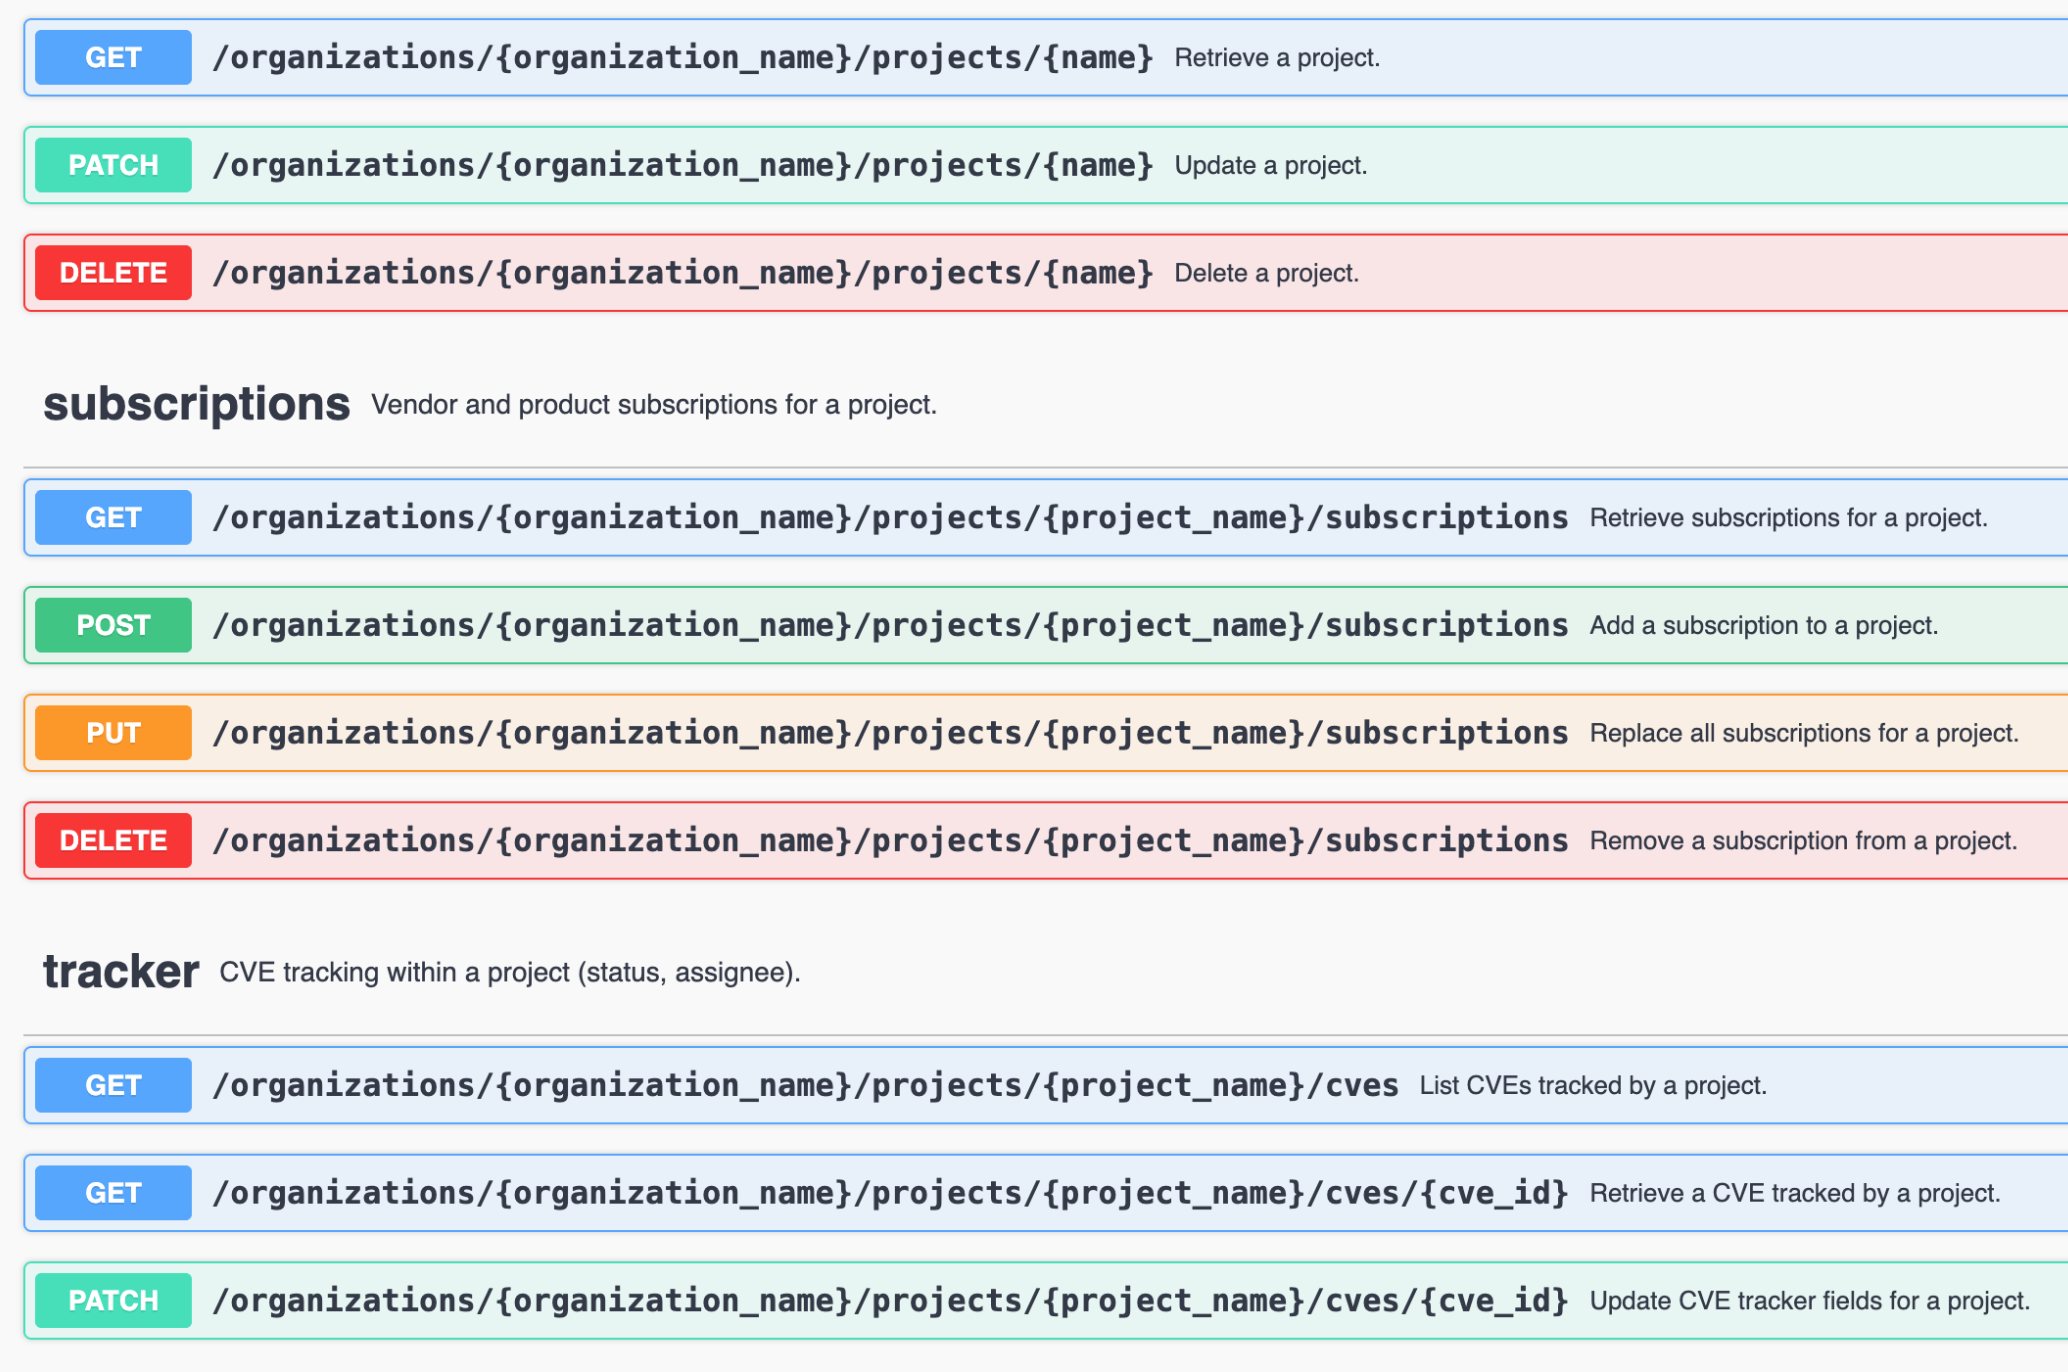
OpenCVE API v2 is now available, with full read and write access to your vulnerability workflows.
List CVEs, manage projects and subscriptions, triage CVEs, and configure automations programmatically. Connect OpenCVE to your own tools and automate the way you monitor and respond to vulnerabilities.
Automations
Jun 12, 2026
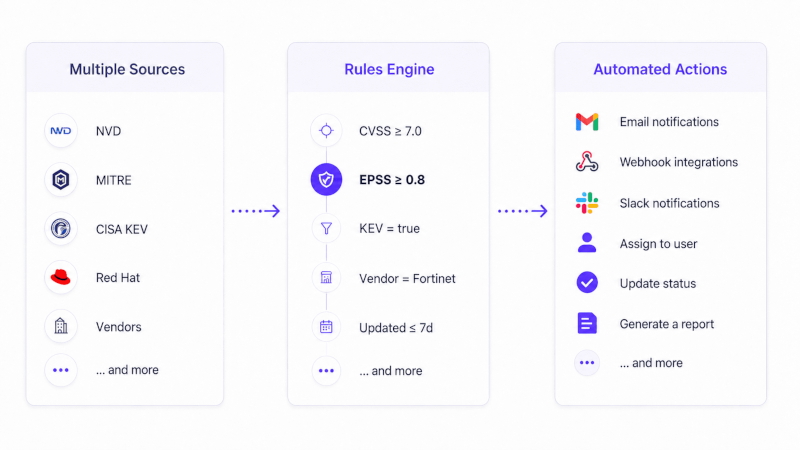
OpenCVE now supports Automations to help teams react faster and reduce CVE noise.
Create alert or report workflows with custom conditions, then trigger actions such as notifications, assignments or status updates when matching CVEs are detected.
MFA Enforcement
Apr 16, 2026
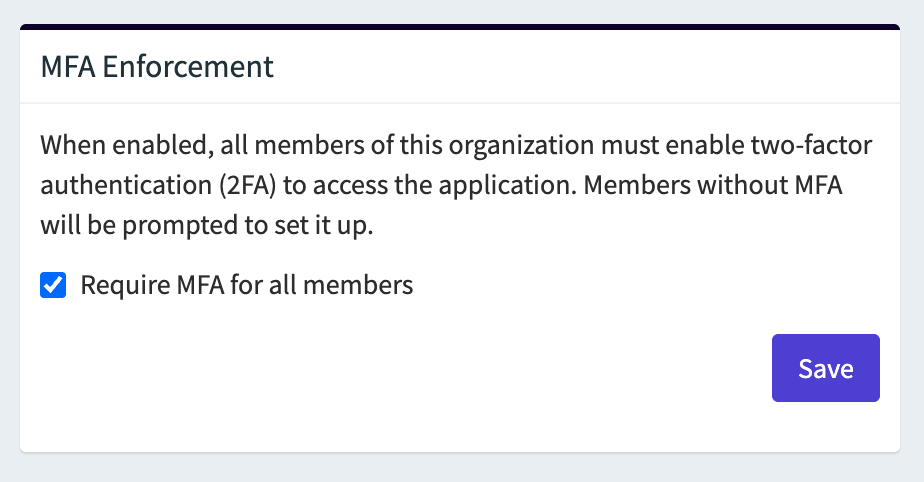
You can now enforce multi-factor authentication (MFA) at the organization level.
When enabled, all members must configure MFA to access the application, improving overall account security. This feature is available in the Pro and Enterprise plans.
SAML 2.0 Single Sign-On (SSO)
Apr 15, 2026
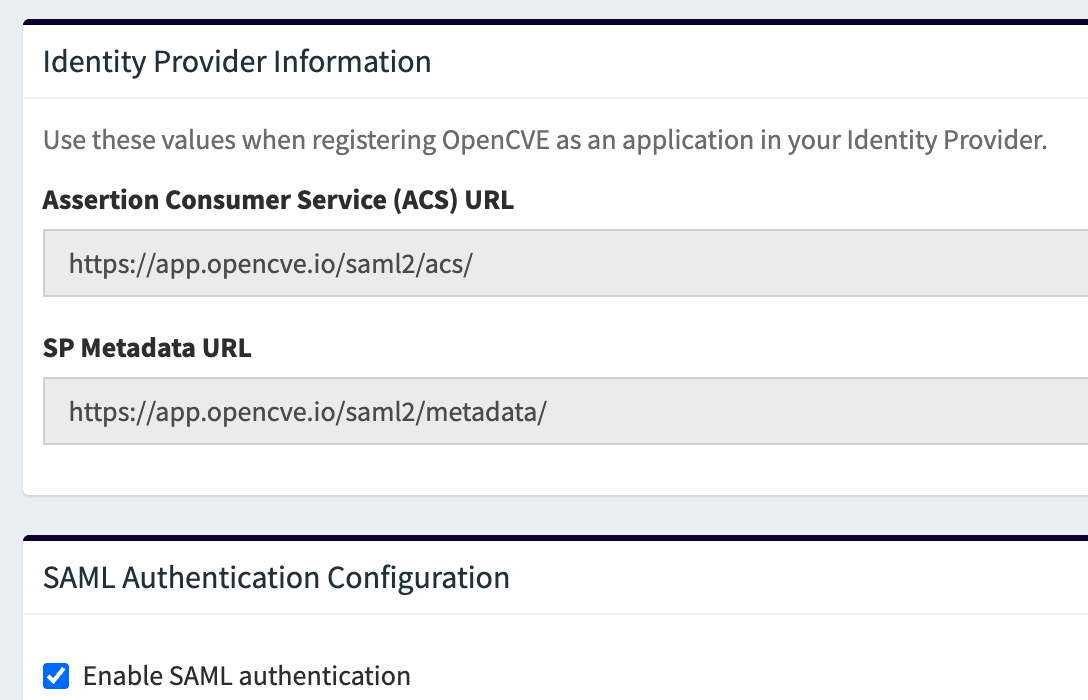
You can now enable SAML 2.0 Single Sign-On (SSO) to let your team authenticate via your corporate Identity Provider (Okta, Azure AD, Google Workspace, etc.).
Automatically provision users on first login, and centralize access control, all from your OpenCVE organization settings. This feature is available in the Enterprise plan only.
Test Notifications
Apr 07, 2026
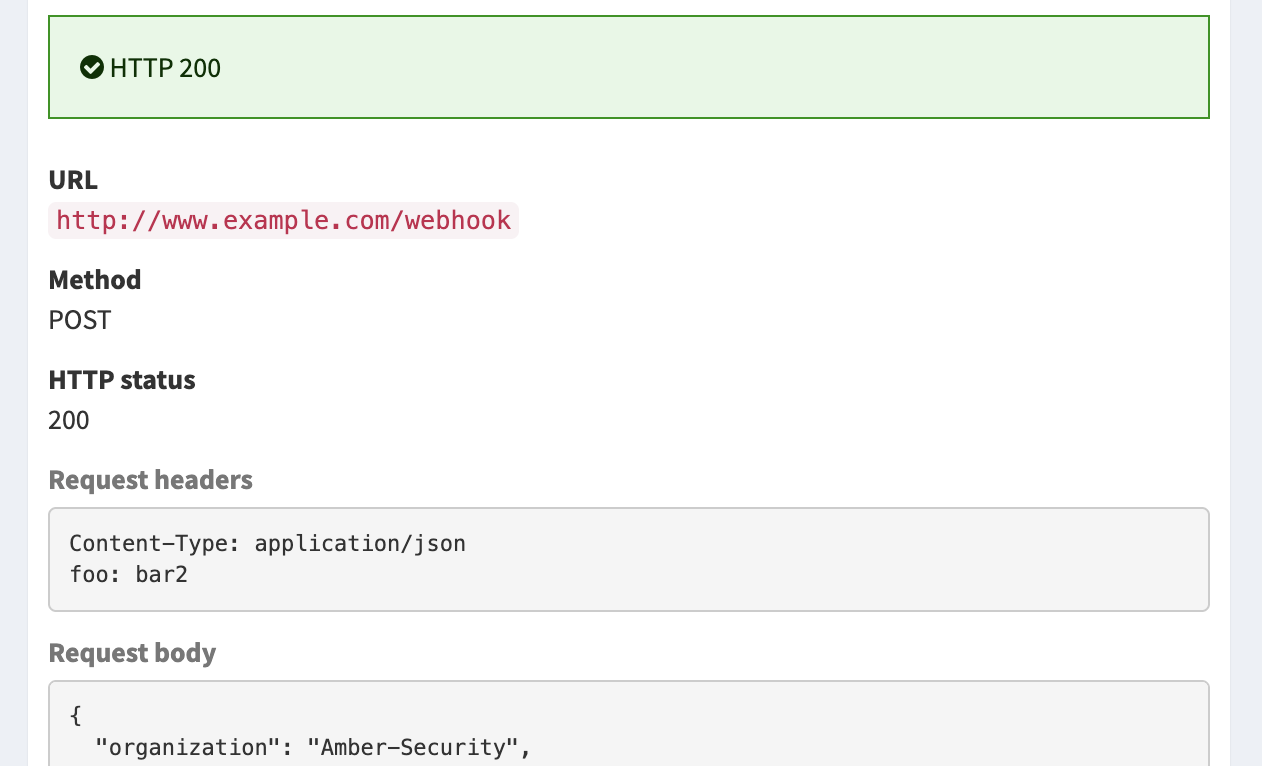
OpenCVE now allows you to send test notifications for your configured channels, including email, Slack, and webhooks.
Quickly verify that your notification settings are correctly set up without waiting for a new CVE to be published.
CVE Comments
Mar 18, 2026
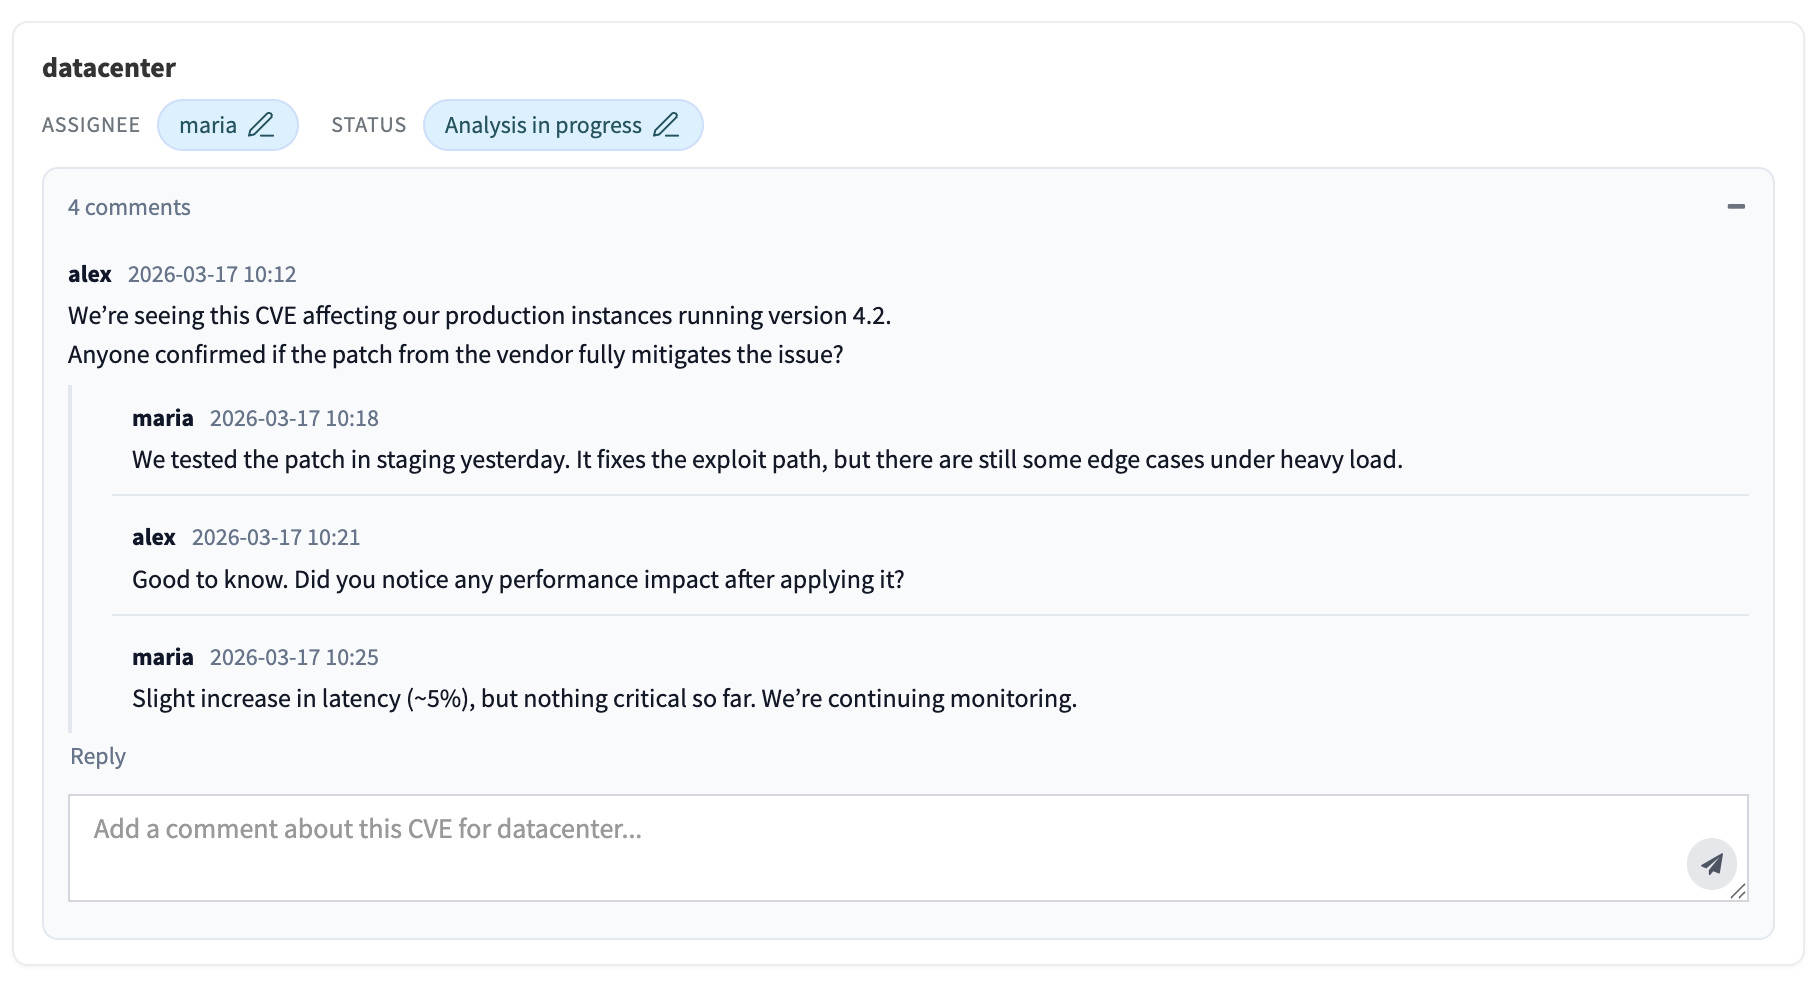
OpenCVE now allows you to add comments to CVEs within your projects. Collaborate with your team by sharing context, analysis, and decisions directly on each vulnerability.
Comments support threaded discussions, making it easier to track conversations, coordinate remediation efforts, and keep all relevant information in one place.
Audit Logs
Mar 10, 2026
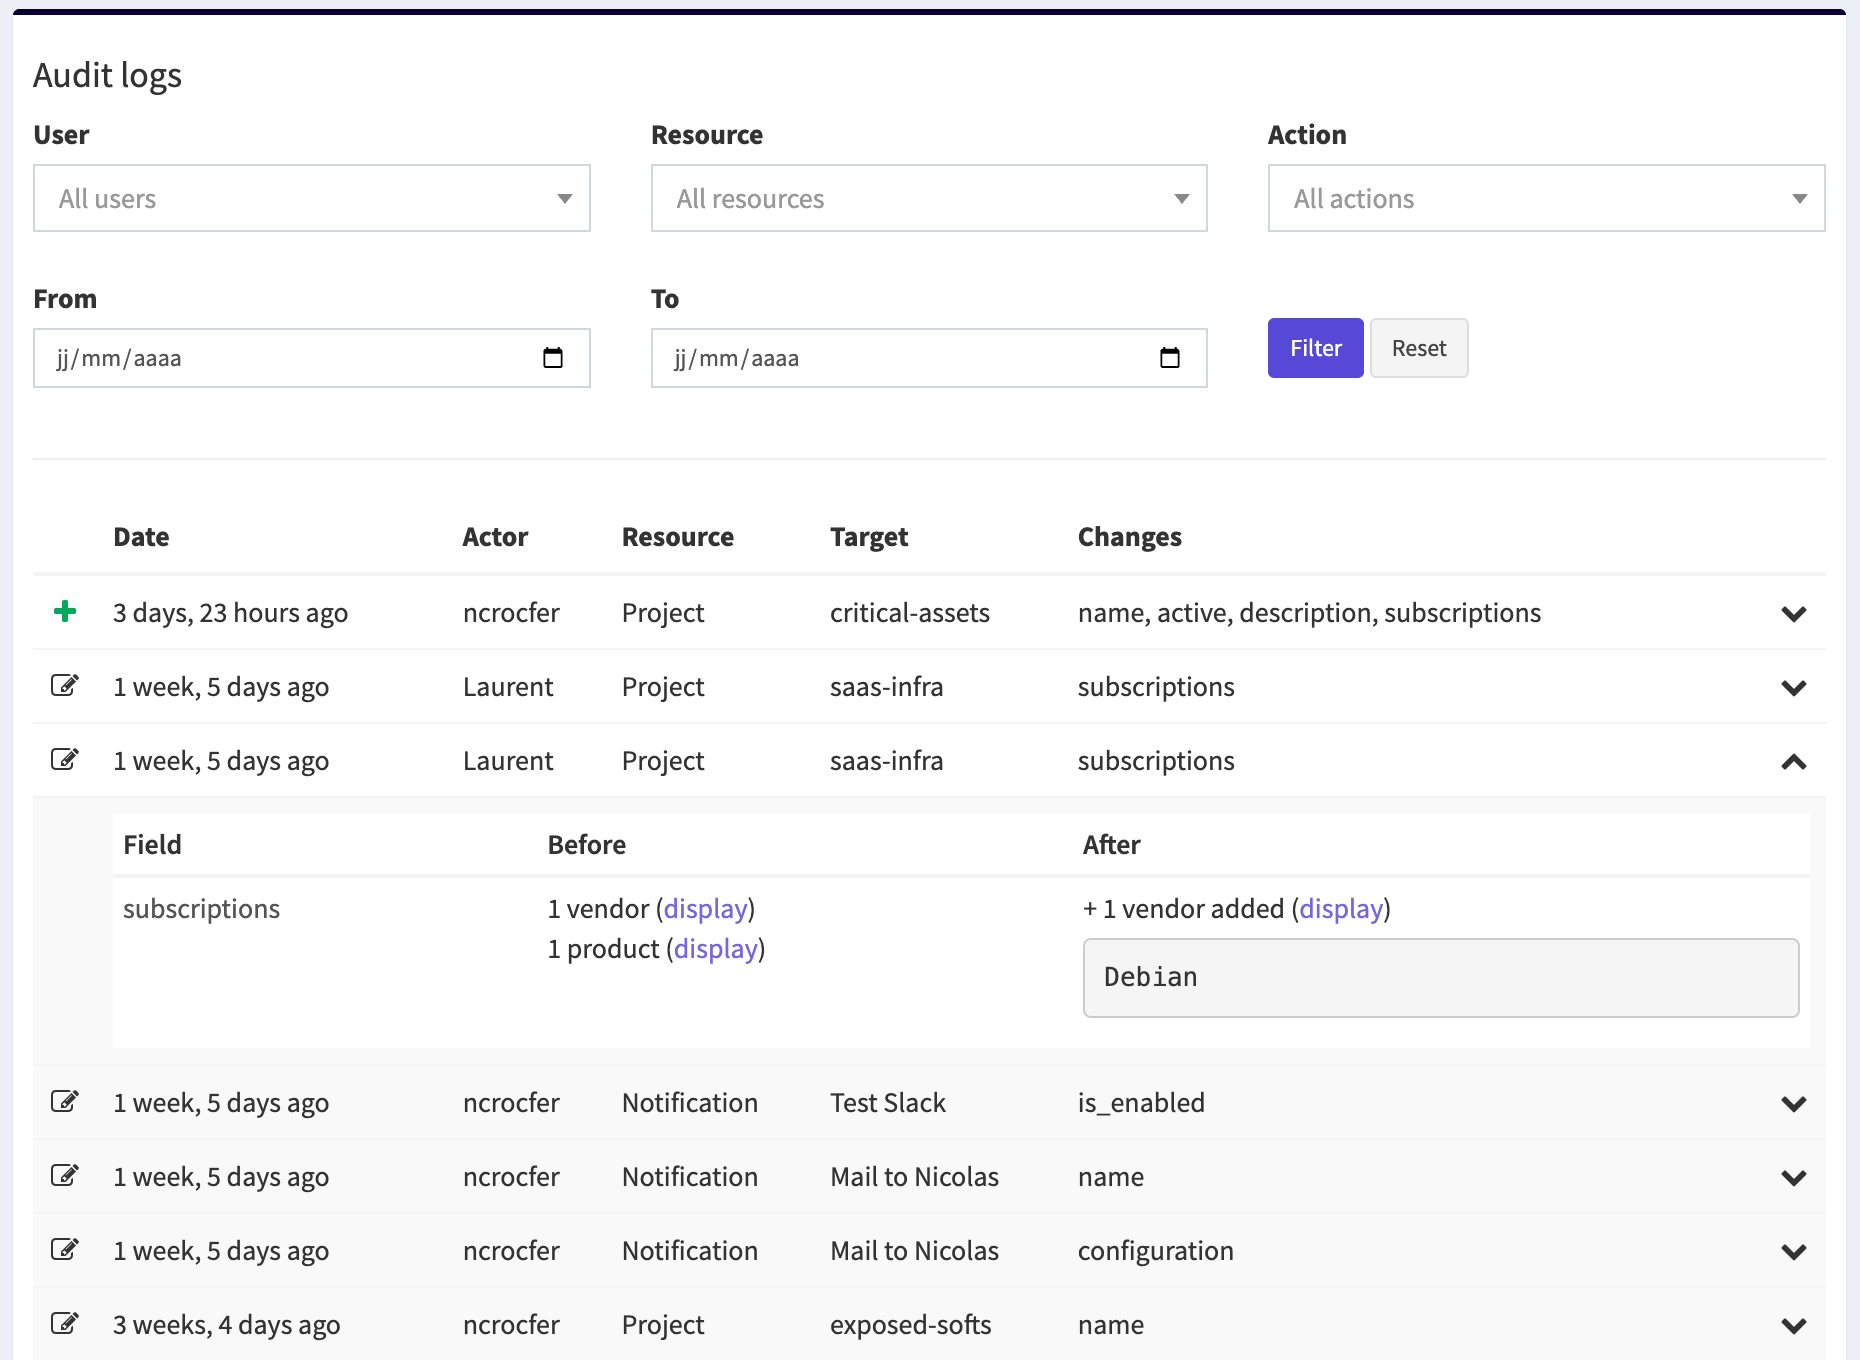
OpenCVE now includes Audit Logs, allowing organizations to track important actions performed within their organization. This feature is available in the Enterprise plan.
Audit Logs provide a detailed history of activity across your organization. For each event, you can see who performed the action, when it happened, and what fields were modified.