
The latest features and improvements of OpenCVE
Subscribe via RSS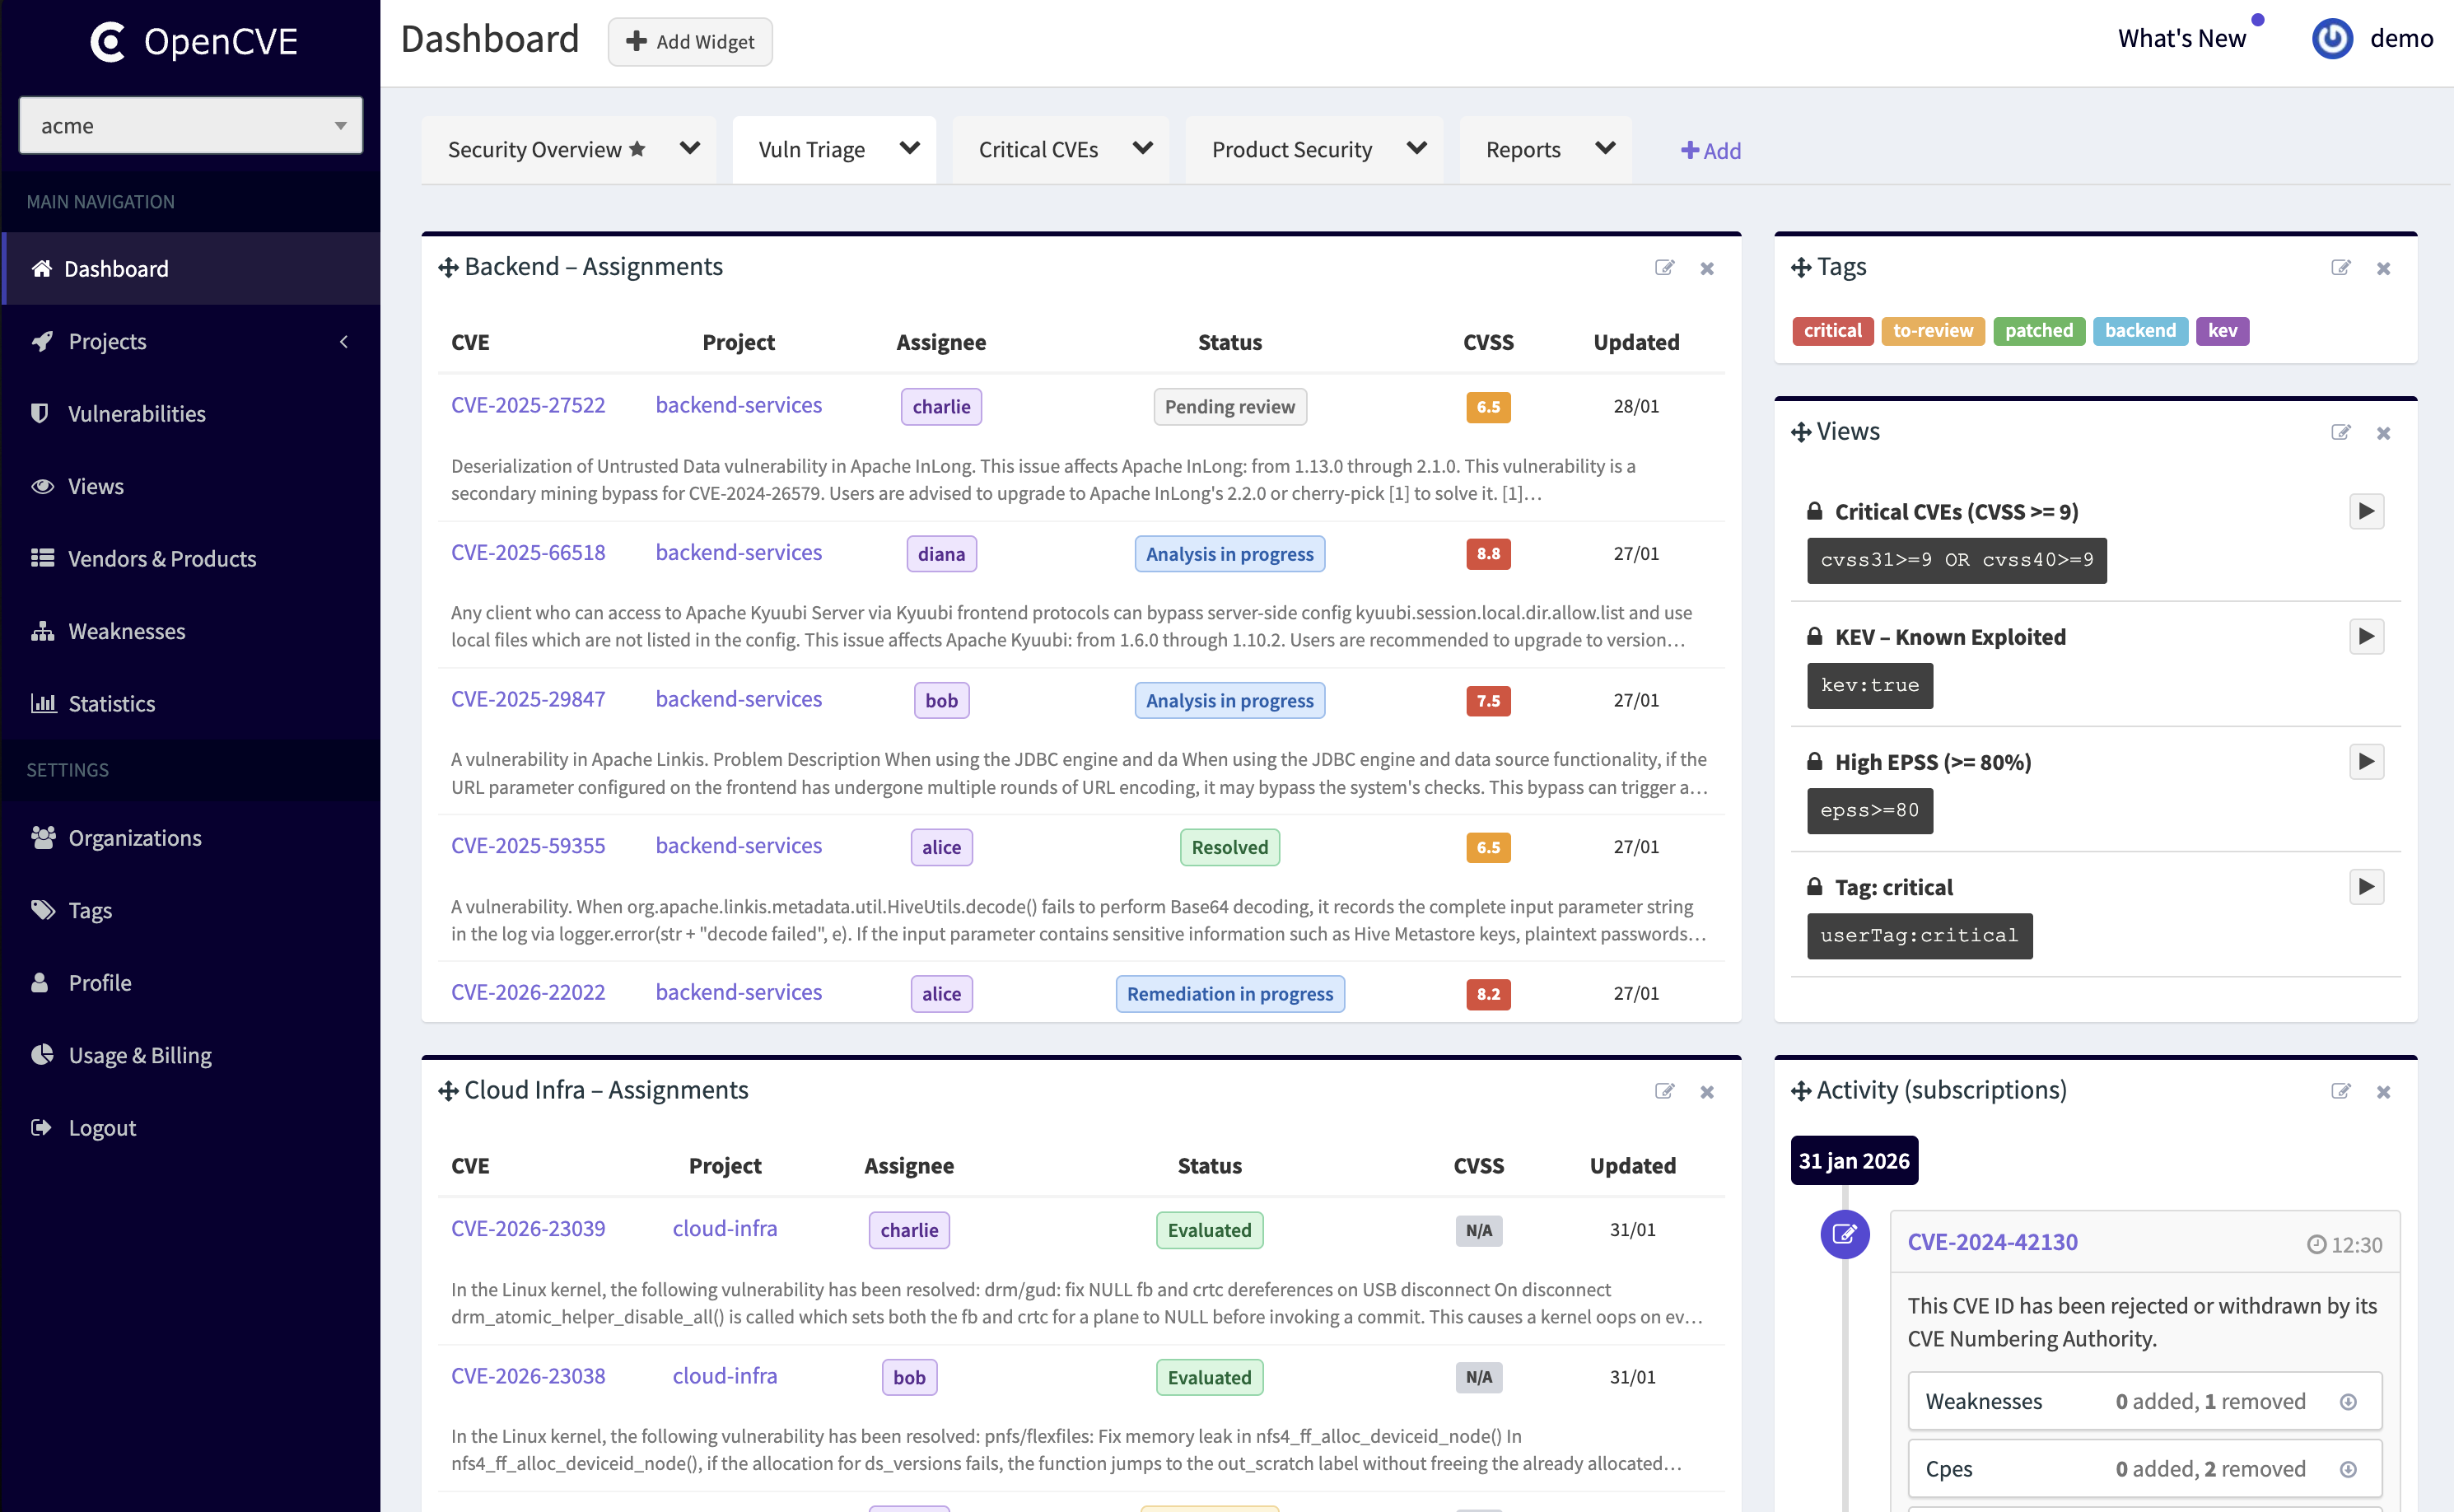
Multiple Dashboards
Feb 12, 2026
OpenCVE now allows you to create multiple dashboards per user. Organize your widgets into separate, custom views for different teams, projects, or workflows.
This makes it easier to monitor CVE activity, triage vulnerabilities, and structure your security insights in a way that fits your operational needs.
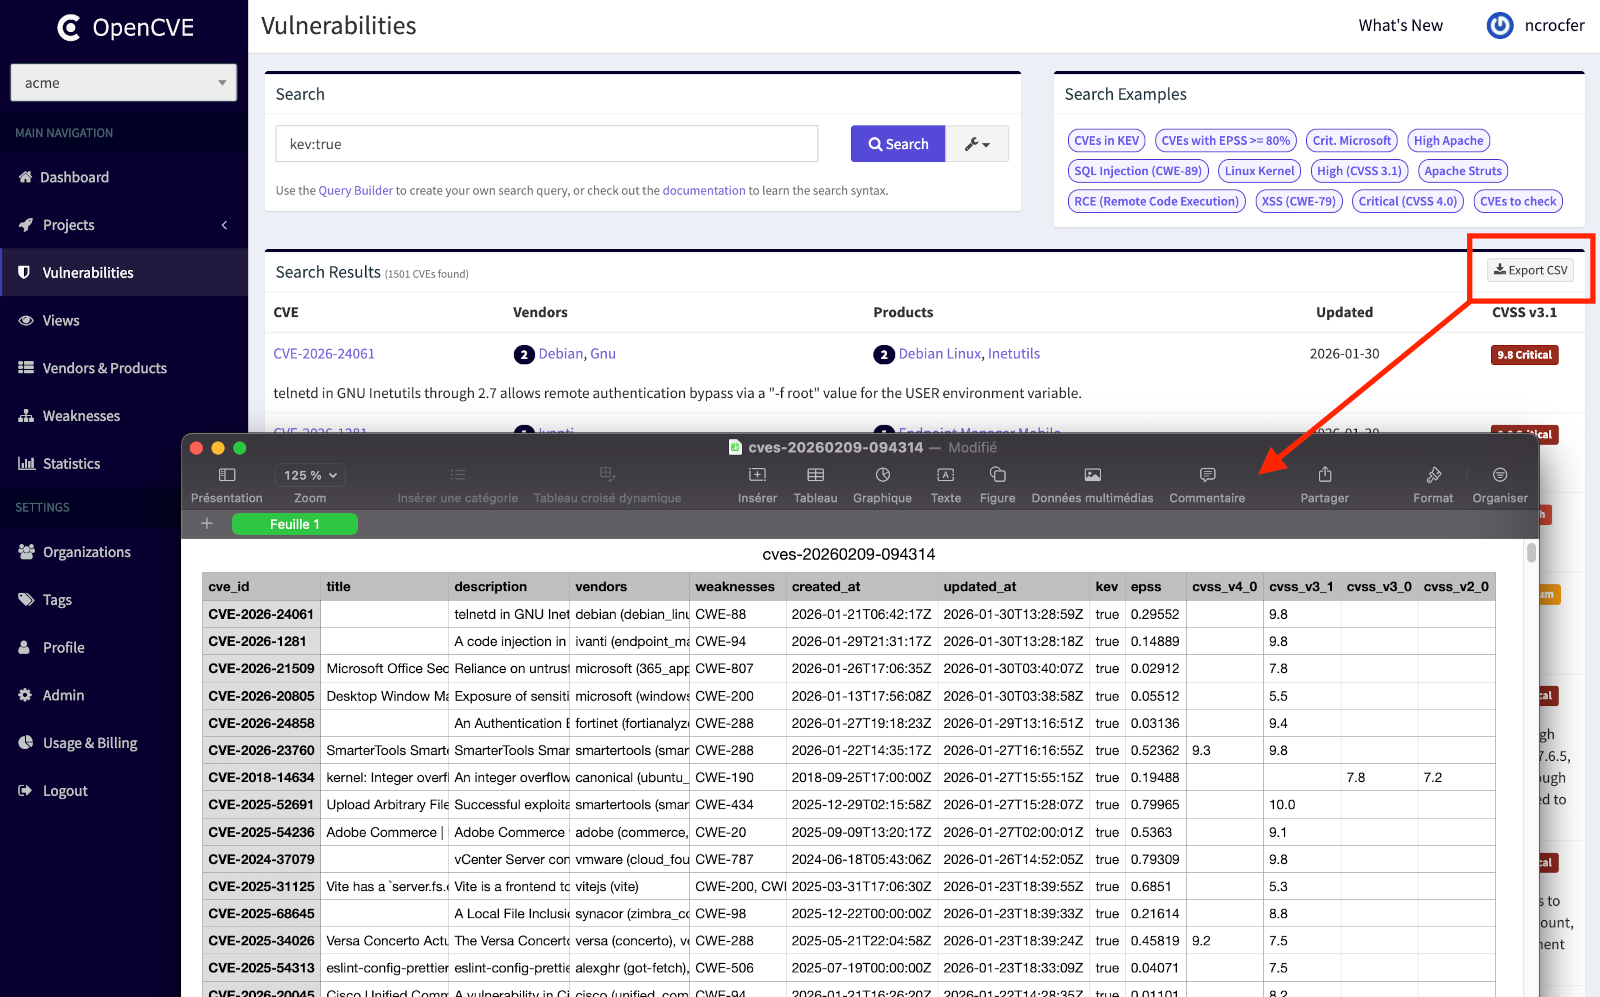
CSV Export for Vulnerabilities
Feb 09, 2026
OpenCVE now allows you to export vulnerability results as CSV files directly from the vulnerabilities list and from each project.
This makes it easy to analyze CVE data in spreadsheets, generate reports, and integrate OpenCVE data with external tools and workflows.
CSV export is available from the Pro plan and above.
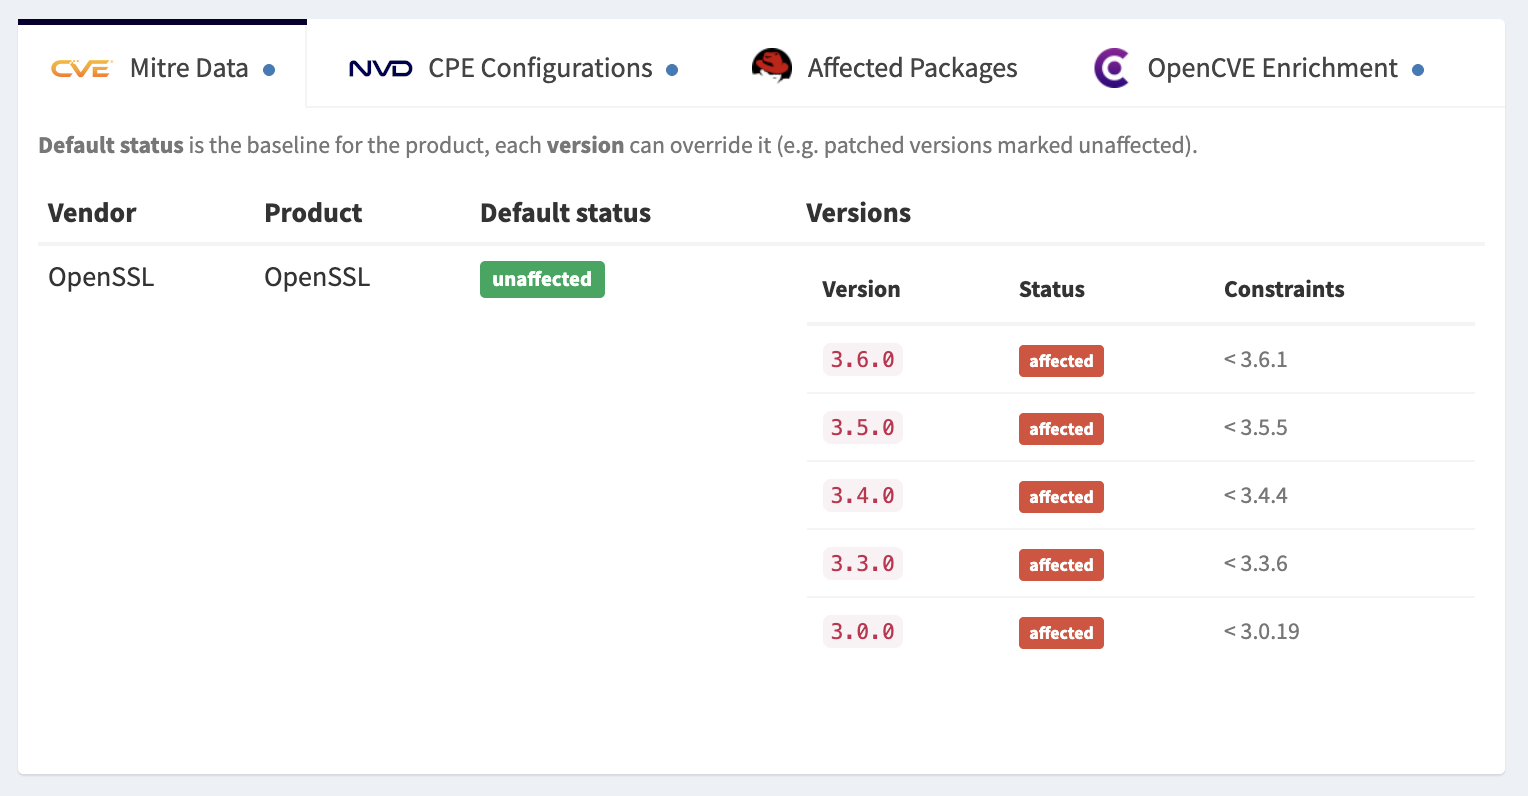
MITRE Affected Products Tab
Feb 03, 2026
OpenCVE now includes a new MITRE tab on the CVE detail page, displaying affected products and versions as provided by the CNA.
This makes it easier to quickly identify impacted product versions without parsing raw CVE data, improving day-to-day vulnerability analysis.
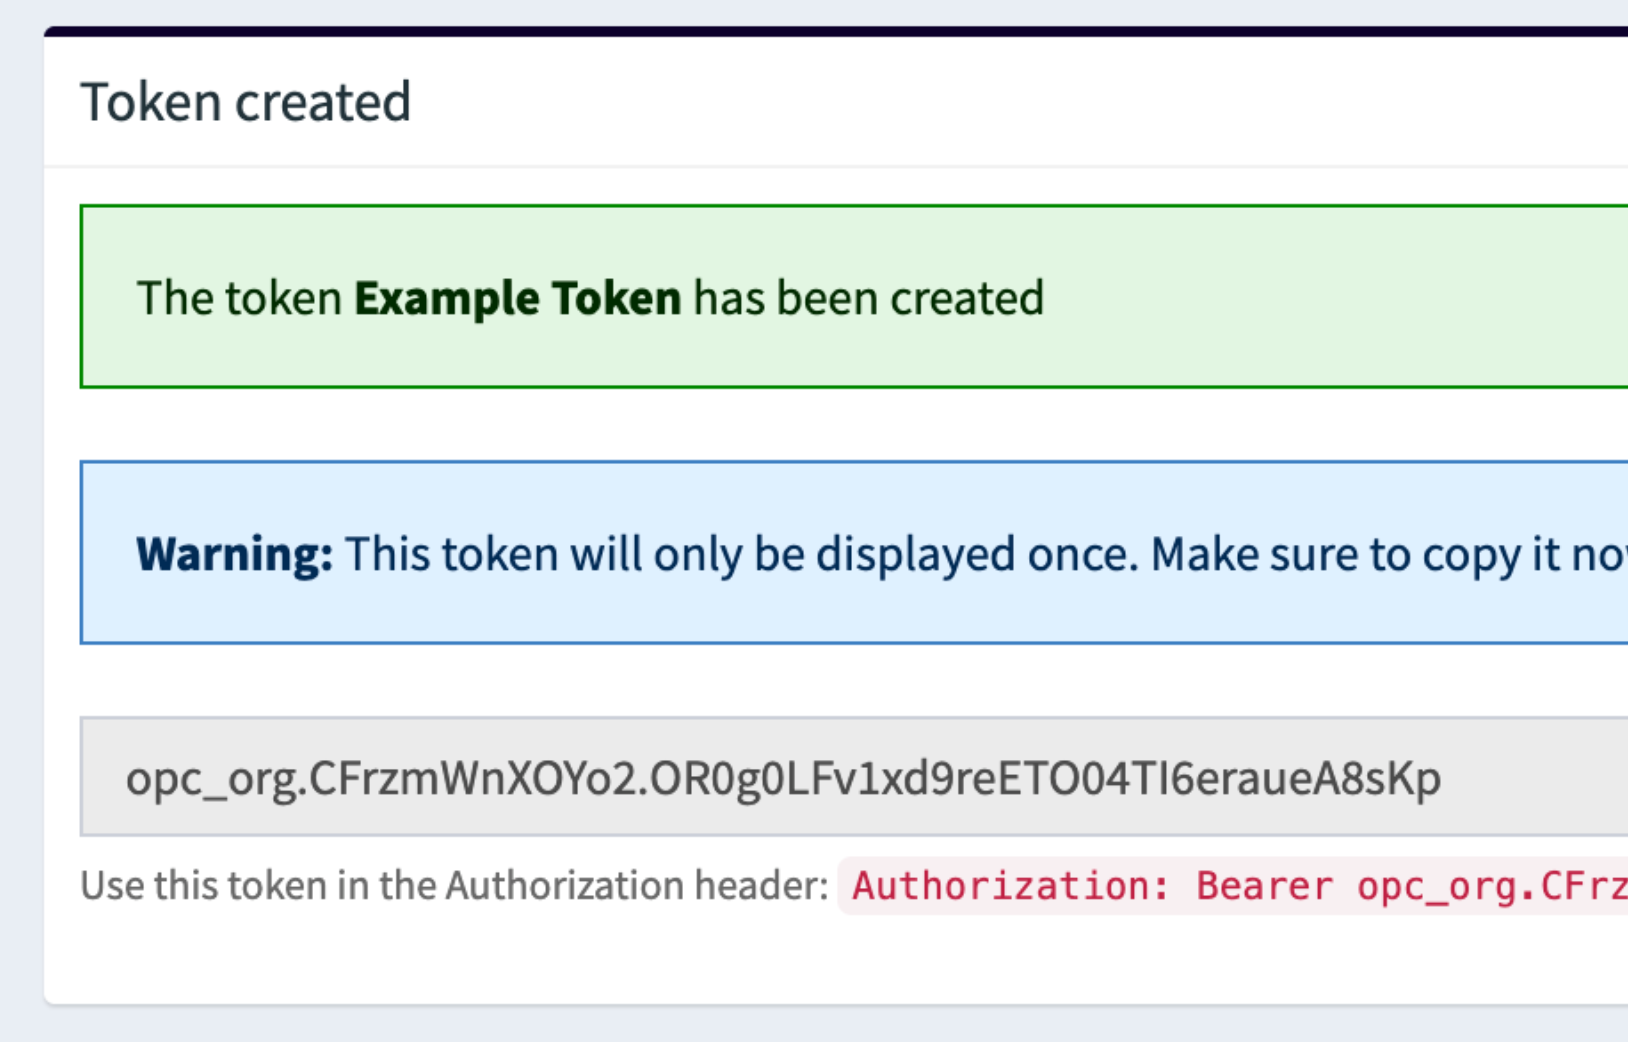
Organization API Tokens
Jan 23, 2026
OpenCVE now supports organization-level API tokens for authenticating API requests in a more secure and flexible way.
Organization tokens are designed for machine-to-machine access and can be safely used in scripts, CI/CD pipelines, SIEMs, and other automation tools. Multiple tokens can be created per organization and revoked at any time without impacting user accounts.
CVE Tracking
Dec 09, 2025
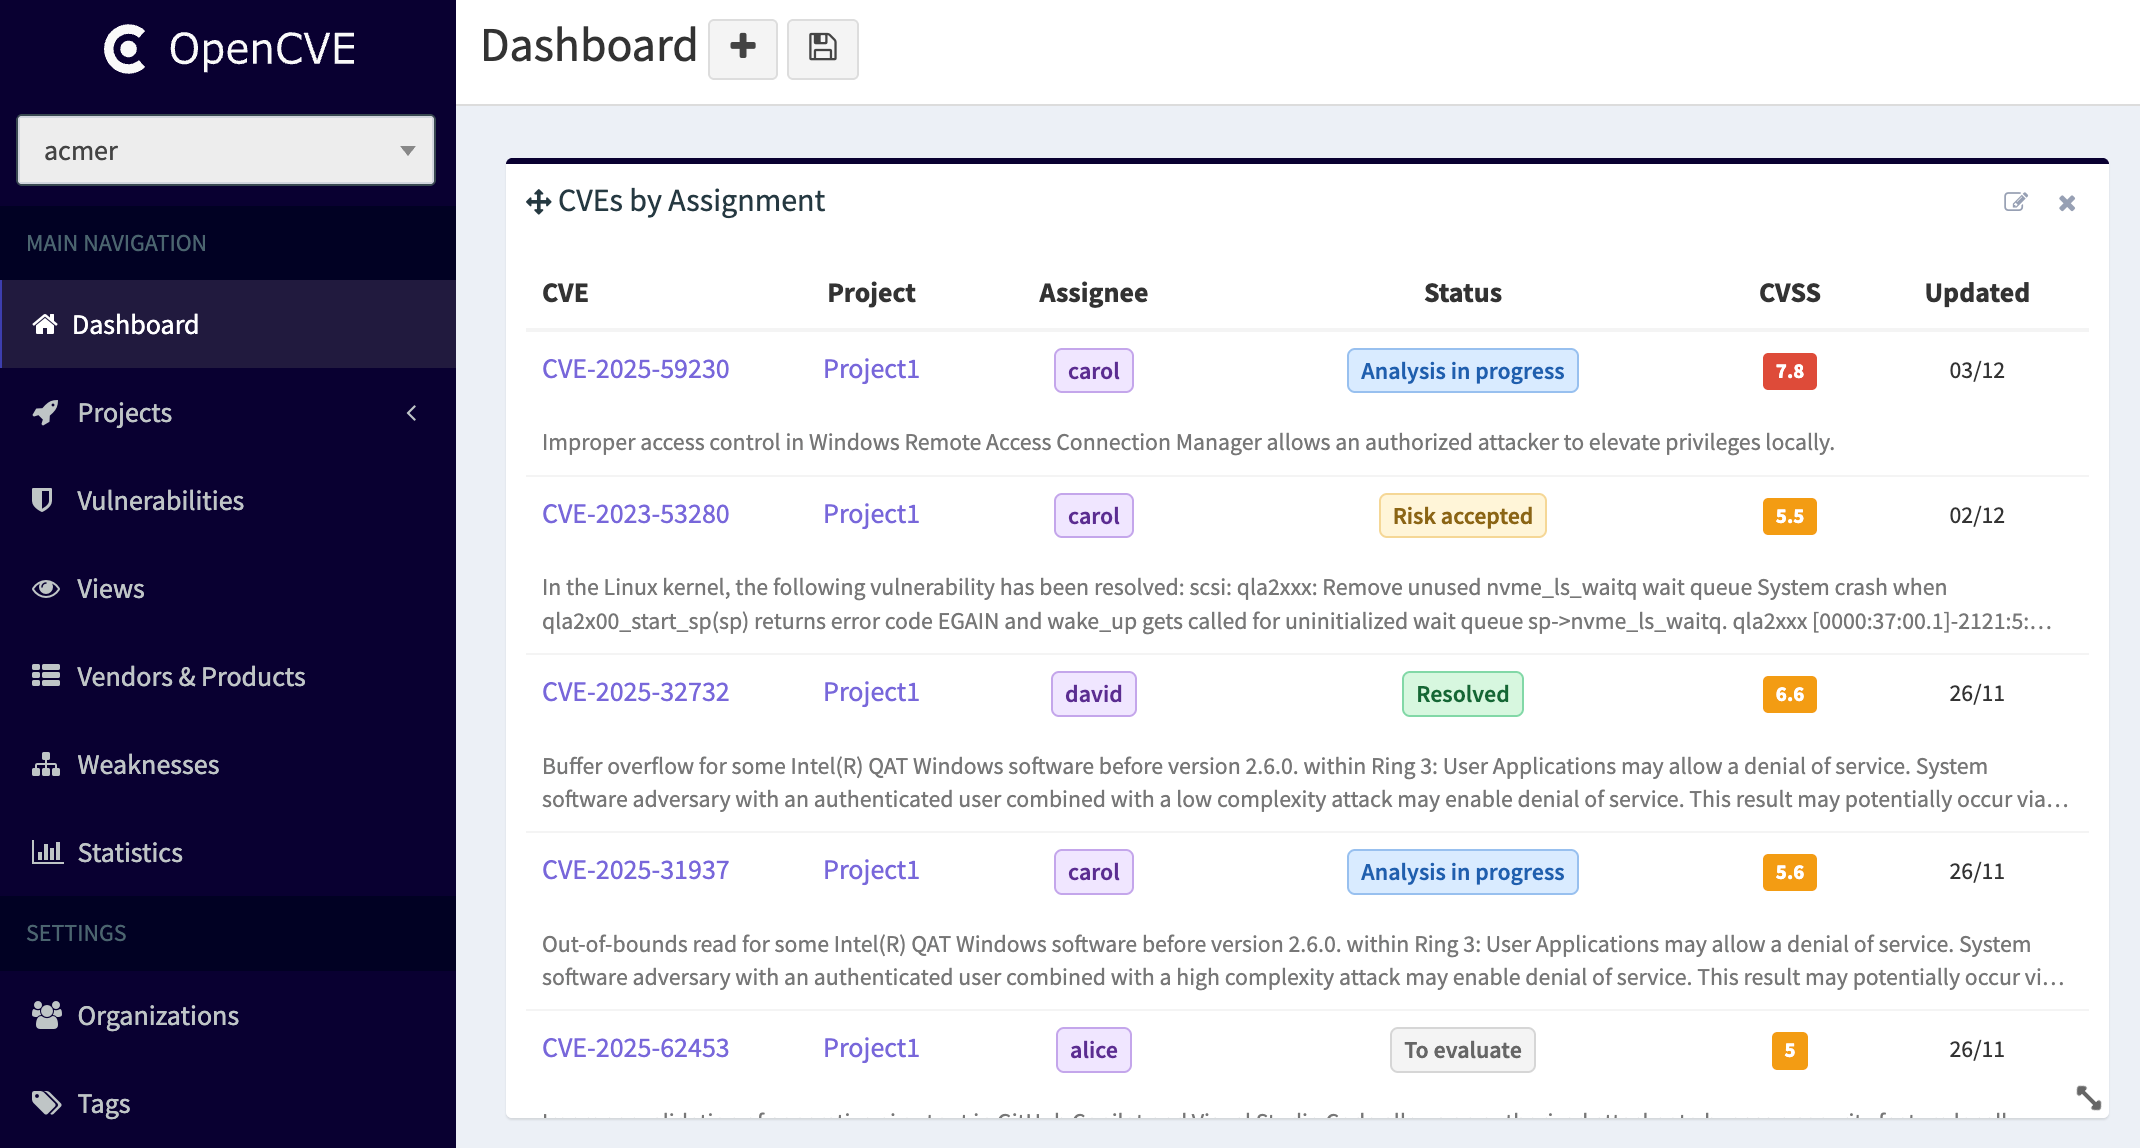
You can now manage vulnerability ownership with the new CVE Tracking feature inside your projects.
Assign users to CVEs and track progress with workflow statuses to bring clarity and accountability to your remediation efforts — directly from the project vulnerability list or inside each CVE page.
Slack Notifications
Nov 04, 2025
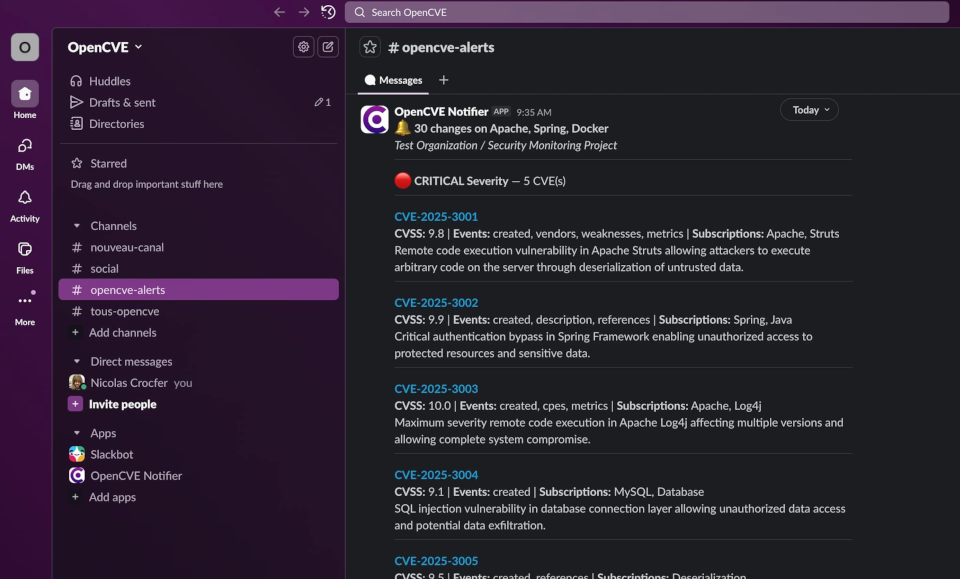
OpenCVE now supports Slack as a new notification channel to stay informed in real time, right where your team collaborates.
In addition to email and webhooks, you can receive instant alerts directly in your Slack workspace when new or updated CVEs impact your subscribed vendors or products.
Date Filters in Advanced Search
Nov 03, 2025
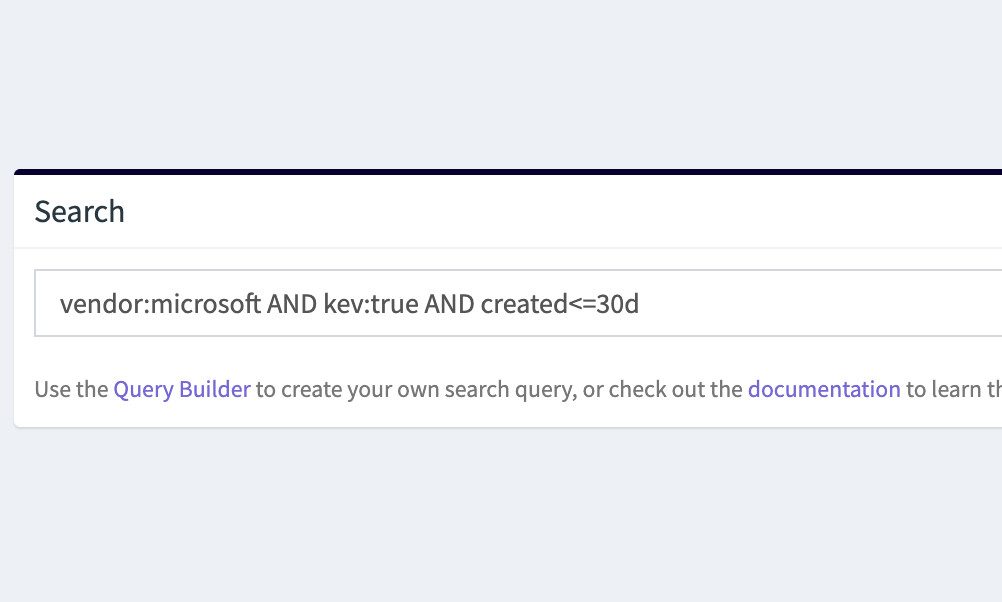
You can now refine your CVE queries using the new created and updated filters. These allow you to search vulnerabilities based on when they were added or modified, for example vendor:microsoft AND kev:true AND created<=30d
.
This makes it easier to focus on the most recent or recently updated vulnerabilities relevant to your environment.
Two-Factor Authentication (2FA)
Oct 31, 2025
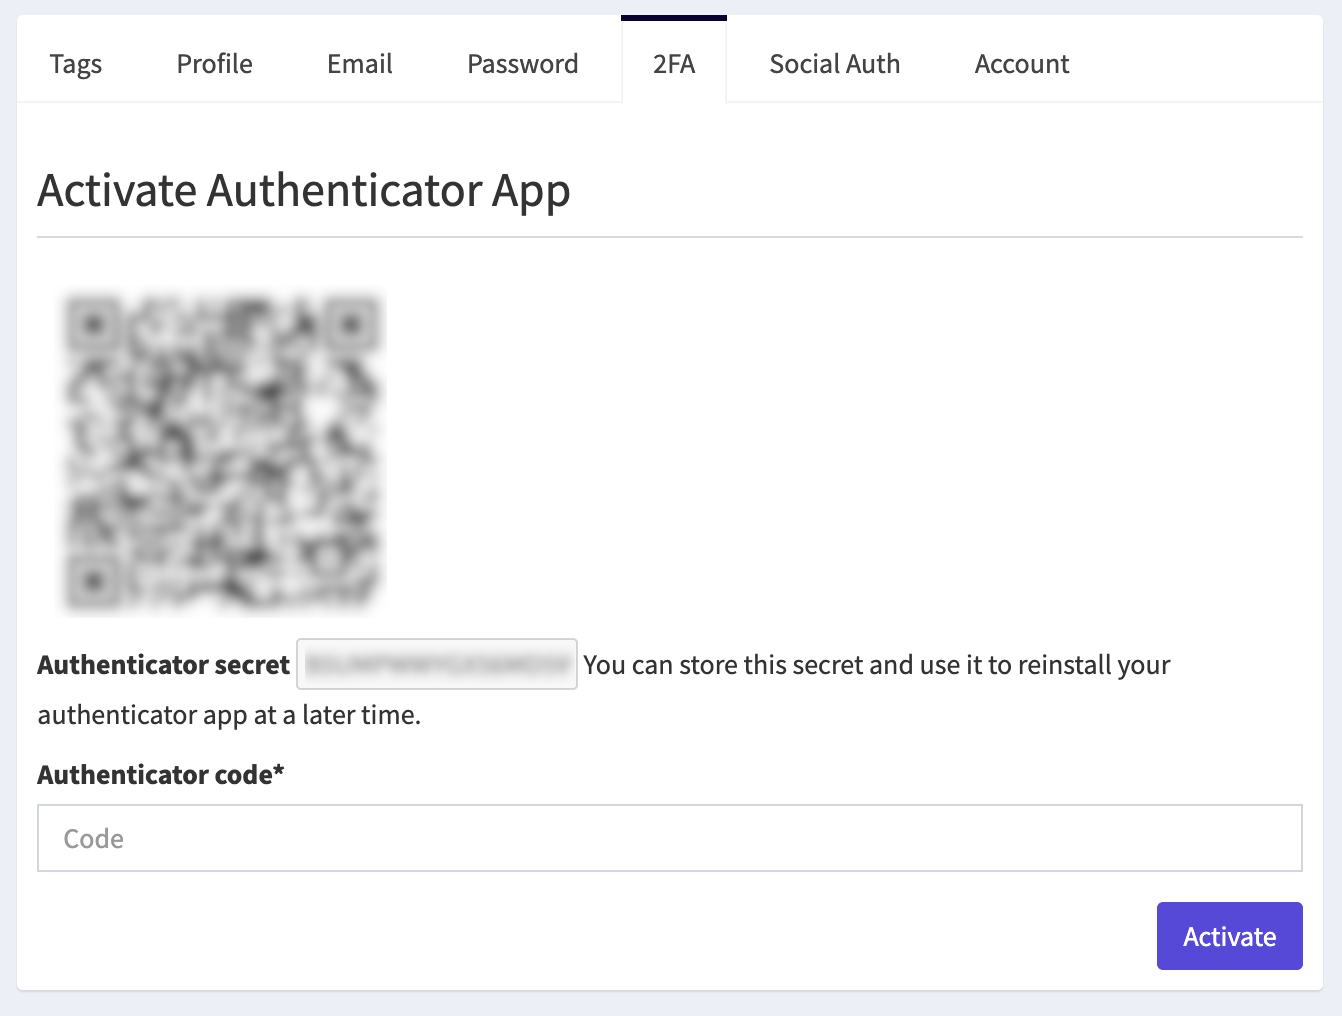
You can now secure your OpenCVE account with Two-Factor Authentication.
Enabling 2FA adds an extra layer of protection by requiring a time-based one-time code, helping prevent unauthorized access even if your credentials are compromised.
You can activate 2FA from your profile settings.
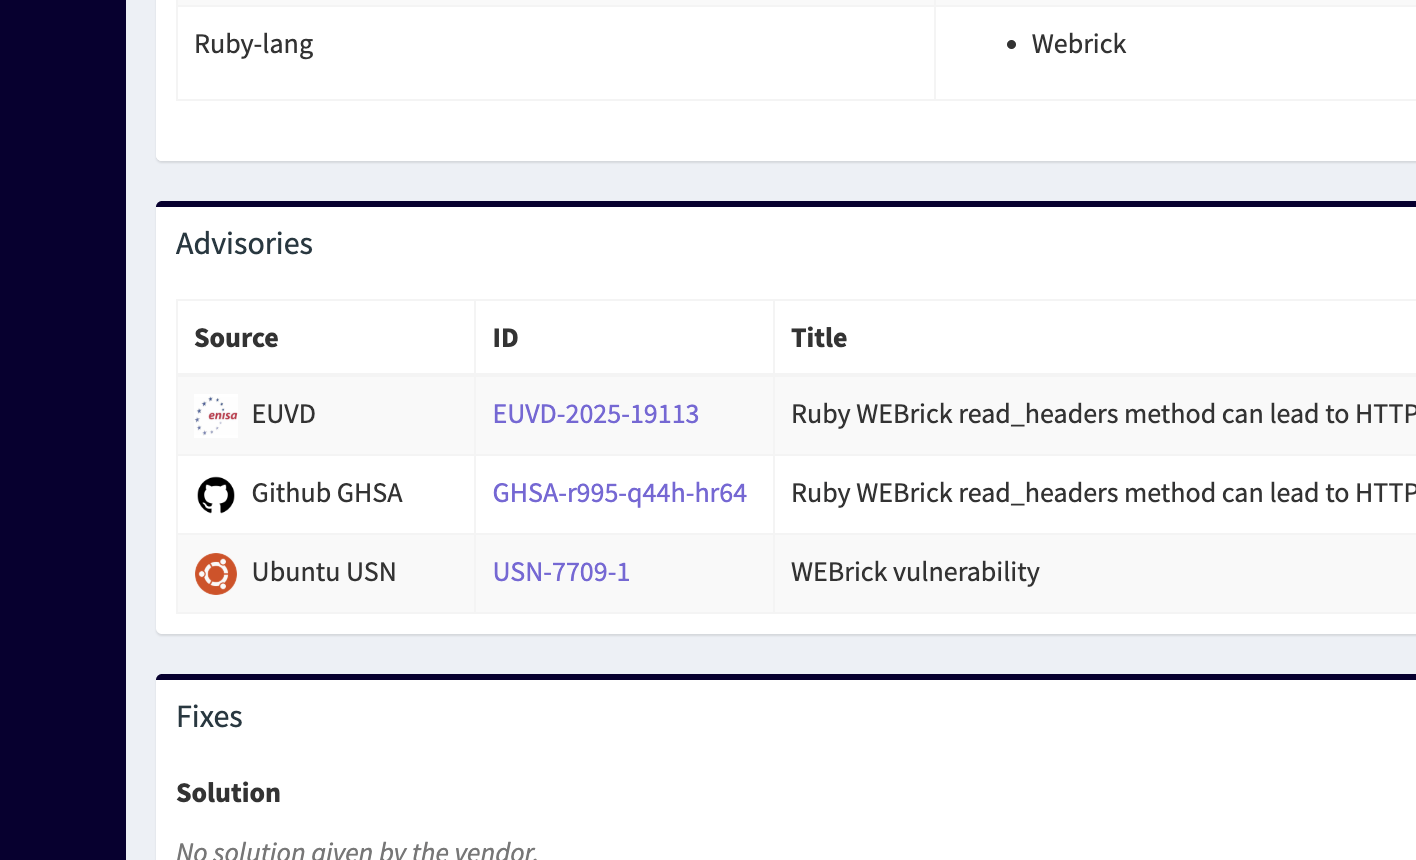
Introducing Advisories
Oct 06, 2025
You can now see which official advisories are linked to each CVE, from sources like EUVD, GHSA, DSA, DLA, and USN.
Each advisory includes a direct link to the original bulletin, helping you quickly access remediation details and official guidance from vendors or distributions.
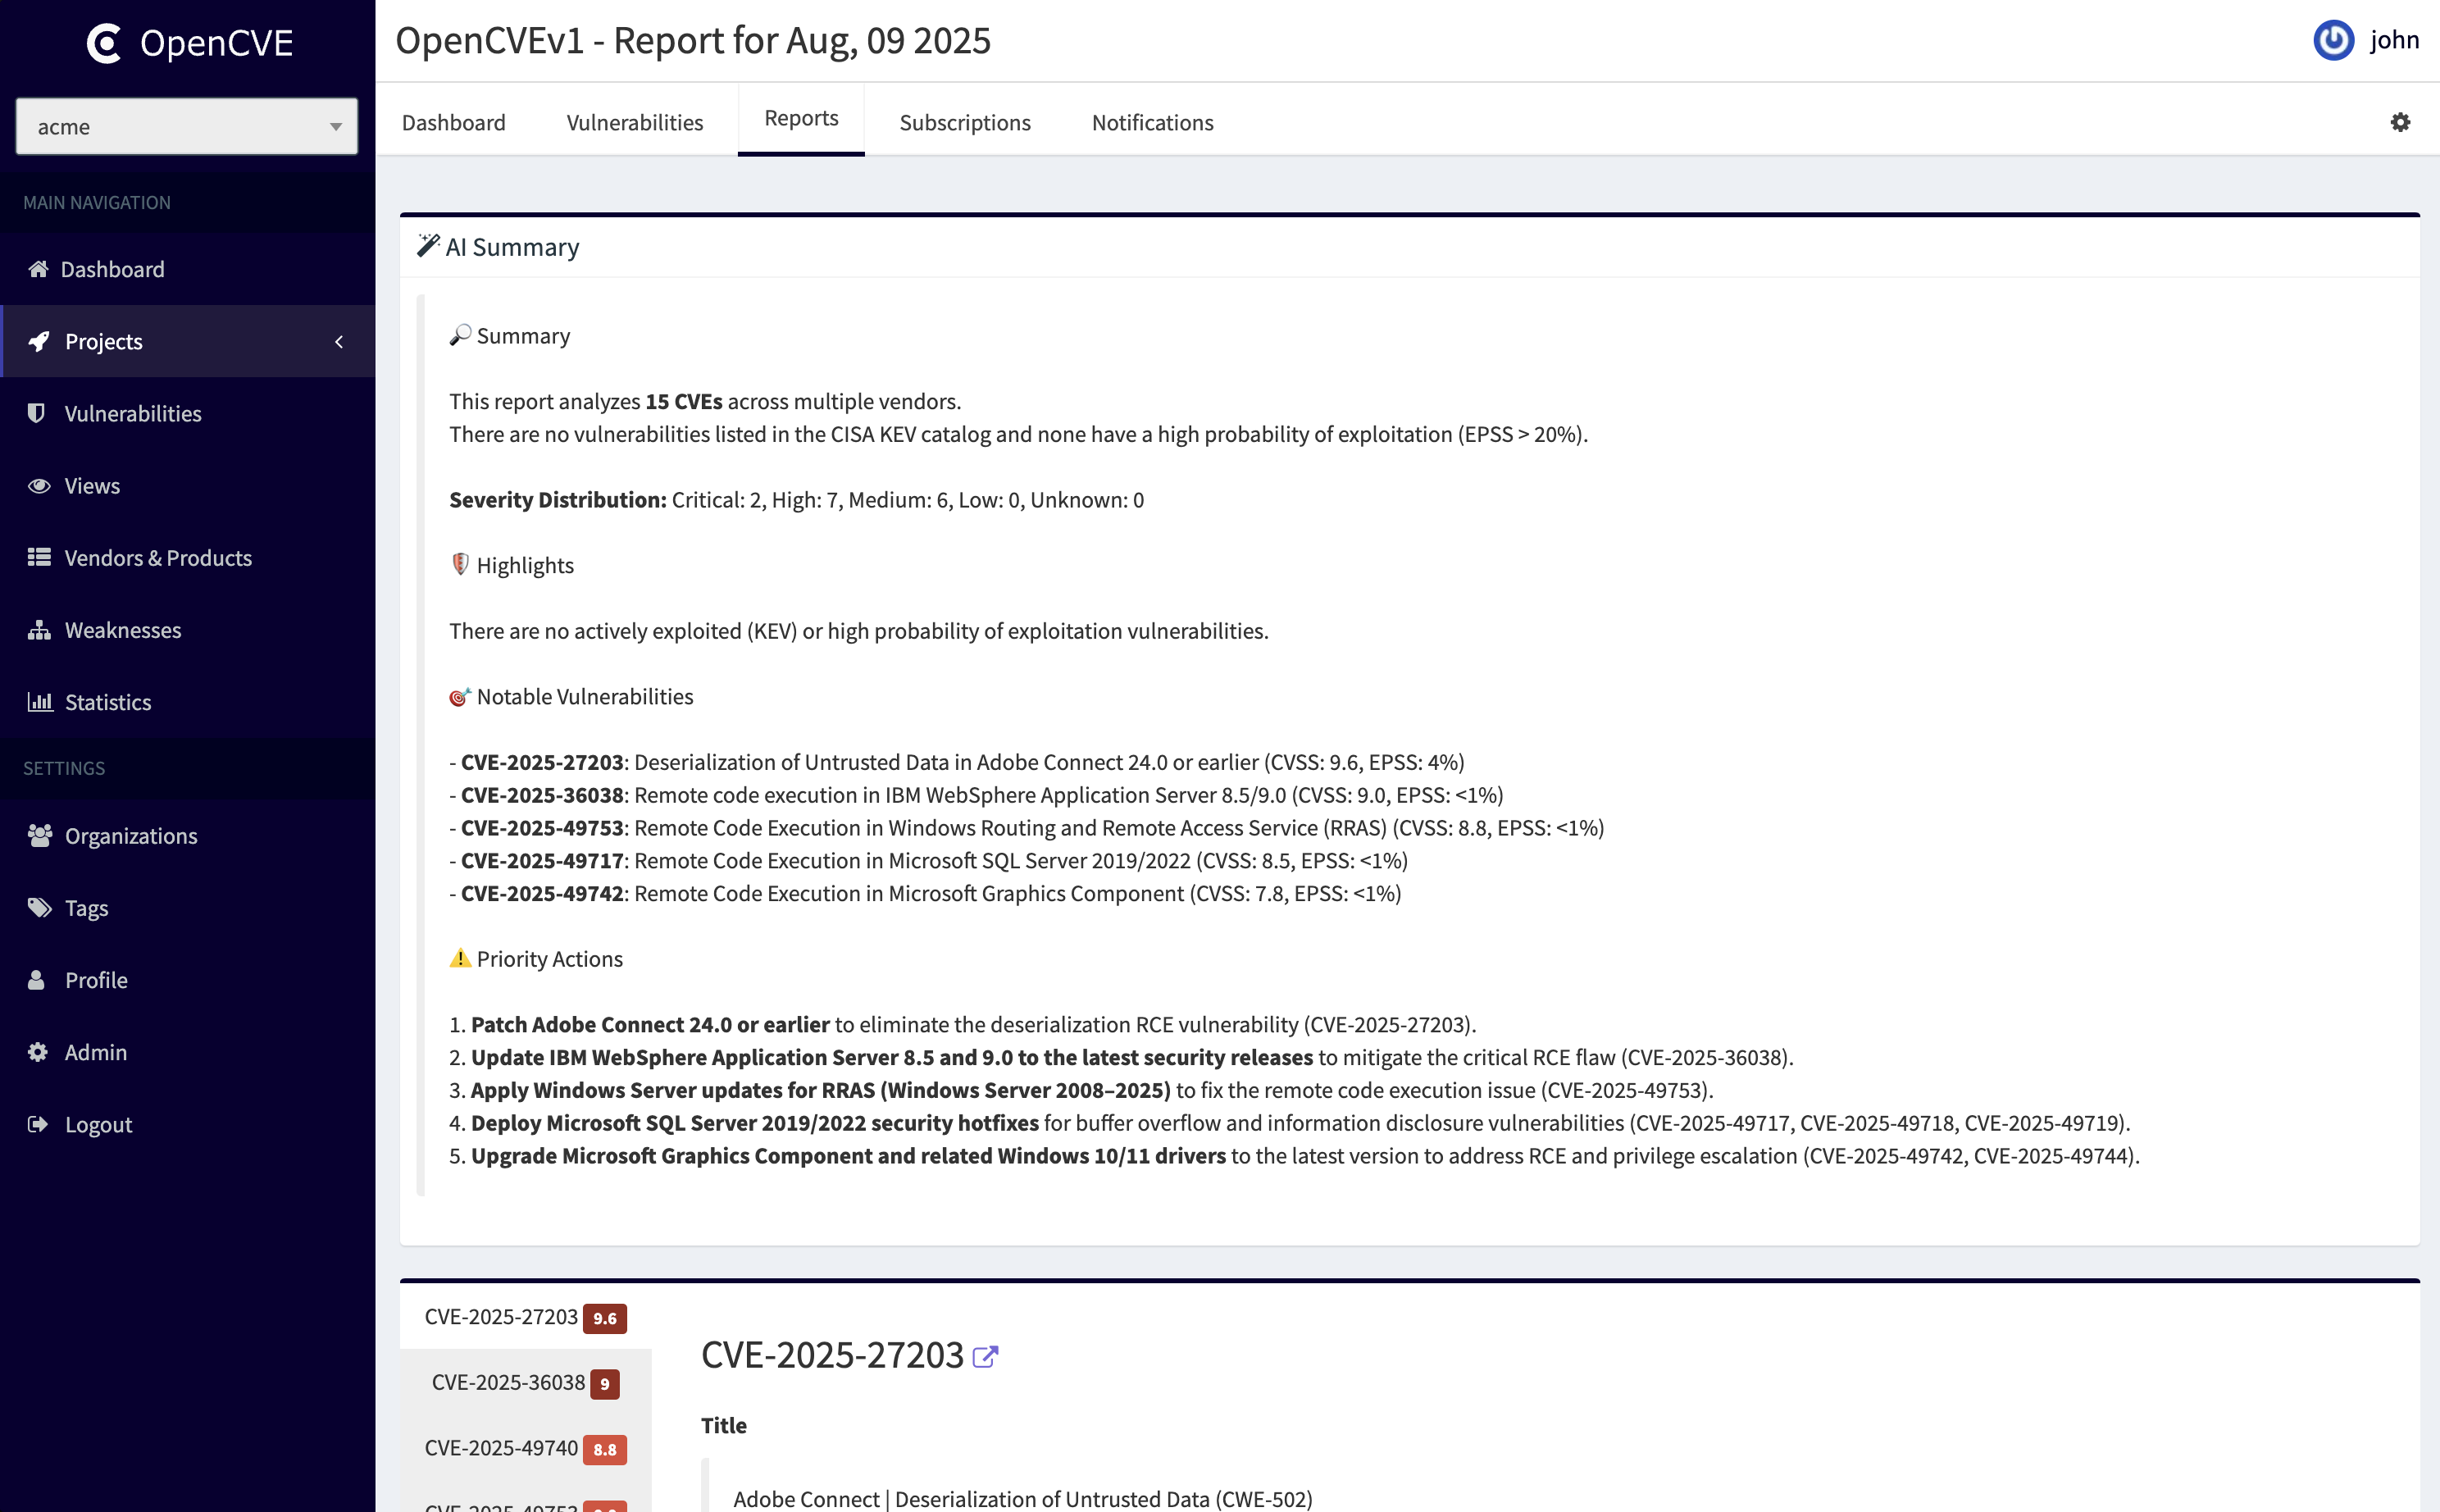
AI-Powered Report Summaries
Sep 02, 2025
Your daily CVE reports are now automatically summarized by a Large Language Model (LLM) every night at 2:00 AM UTC. Get concise insights on the latest vulnerabilities, save time reviewing changes, and focus on what matters most for your projects.
Available on OpenCVE.io for Starter, Pro, and Enterprise plans.